
Asep Darmawan
- Artificial Intelligence
- October 22, 2026
- 8 views
The End of the Patching Treadmill: Shifting from Vulnerability Counts to Risk-Based Exposure Management
In the modern enterprise, the IT security department has long been trapped in an infinite loop: scan, report, patch, repeat. Yet, despite record-breaking investments in cybersecurity, the backlog of vulnerabilities…
- Data Privacy and Ethics
- September 28, 2026
- 87 views
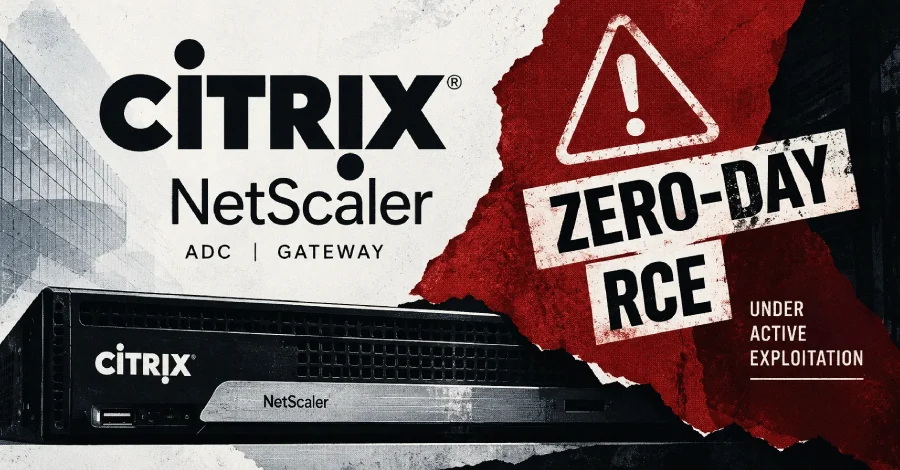
Critical Zero-Day Exploits Strike Citrix NetScaler ADC and Gateway: Urgent Patching Required
By Swati Khandelwal | September 27, 2026 In a major escalation of network security threats, Citrix (a brand under the Cloud Software Group) has officially confirmed that two critical vulnerabilities…
Dwi Wanna
- Data Privacy and Ethics
- August 24, 2026
- 71 views
The Escalating Threat Landscape: AI-Powered Industrial Sabotage and the Patching Crisis of August 2026
By Ravie Lakshmanan August 24, 2026 The digital landscape has entered a period of deceptive calm, where the most dangerous threats often masquerade as mundane background processes. A package installation,…
Raul Delapena Setiawan
- Data Privacy and Ethics
- August 8, 2026
- 64 views
The AI Paradox: Why Automated Security Patching Is Currently a Liability
As the digital ecosystem becomes increasingly saturated with AI-generated code, a growing chorus of cybersecurity experts is sounding the alarm. While the promise of artificial intelligence in defense—specifically its ability…


 Reynand Wu

 Sagoh


 Azzam Bilal Chamdy

Beyond the Transaction: How to Transform Your Email List Into a Thriving Community
Ali Ikhwan
- October 24, 2026
- 1 views
