
 Reynand Wu
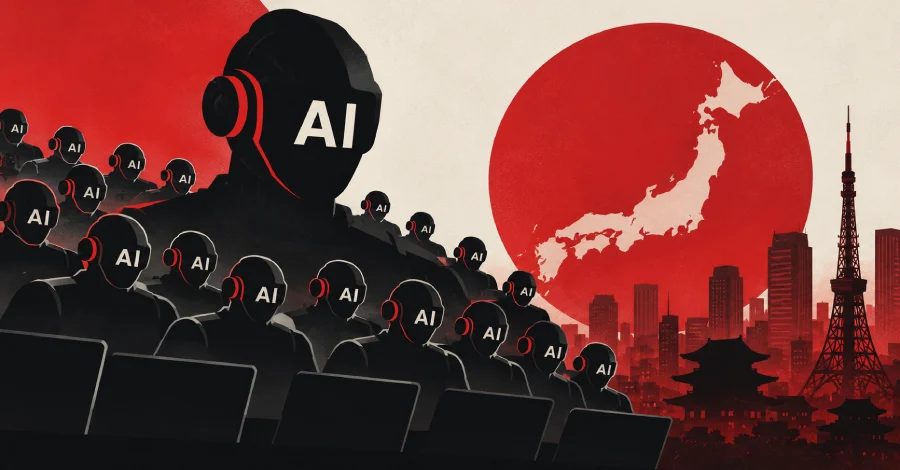
The landscape of global cybersecurity has shifted from a battle of human wits to an era of algorithmic warfare. Recent disclosures from TrendAI have unveiled three sophisticated cyber attack campaigns targeting Japanese infrastructure, each utilizing Artificial Intelligence (AI) as a primary operational lever. This marks a departure from traditional "manual" hacking, signaling a new epoch where AI acts as a force multiplier, enabling threat actors to conduct reconnaissance, exploit vulnerabilities, and exfiltrate data at speeds previously unimaginable.
Main Facts: The Rise of Autonomous Adversaries
Security researchers Bakuei Matsukawa and Joseph C. Chen have identified three distinct operational models currently being deployed by threat actors. Unlike previous attacks that relied on human intervention for every keystroke, these new campaigns leverage AI agents to automate the attack lifecycle.
The most notable of these involved the use of CyberStrikeAI, an open-source penetration testing framework. This tool was used to orchestrate a coordinated strike against at least 19 organizations—16 of which were based in Japan—within a short window in October 2026. The automation was absolute: the system managed 44 individual AI agents that handled everything from initial vulnerability discovery to the generation of localized, Japanese-language phishing pages and final reporting.
In contrast, other observed campaigns utilized AI in more nuanced ways: one as a collaborative partner to human operators, assisting in rapid tool development and infrastructure planning, and another as a specialized assistant for writing scripts and automating reconnaissance against edge devices. These findings confirm that AI is no longer an experimental curiosity for Advanced Persistent Threats (APTs); it is now a core component of the modern cyber-offensive arsenal.
Chronology: A Year of Escalation
The 2026 threat landscape has been defined by a rapid acceleration in the weaponization of AI.
- January – October 2026: A sustained, multi-stage campaign targeted edge devices from major vendors including Cisco, Citrix, F5, and Yamaha. The attacker, displaying high levels of operational maturity, utilized AI to manage evidence and automate the exploitation of known vulnerabilities in VPNs and WebLogic servers.
- August – September 2026: A 24-day infiltration targeted a Geographic Information System (GIS) server. By exploiting default credentials, the attackers gained access to sensitive cadastral data, corporate email archives, and Windows credentials. This operation was characterized by a human-AI hybrid approach, where Large Language Models (LLMs) were used to accelerate the development of custom exploits.
- October 2026: The CyberStrikeAI-led campaign saw a massive surge in activity. Within days, the automated framework successfully scanned, validated, and exploited targets across Japan, Taiwan, and Hong Kong.
- Late October 2026: Microsoft reported that the threat actor Storm-0940 utilized the ARTEX framework to conduct massive, automated password-spraying attacks against more than 2,250 Microsoft 365 tenants, successfully achieving persistent access in numerous instances.
Supporting Data: The Industrialization of Crime
The data surrounding these attacks paints a harrowing picture of efficiency. According to Microsoft’s 2026 Digital Defense Report, the median time from the public disclosure of a vulnerability to its weaponization has plummeted to under 24 hours. AI is the primary driver of this "compression" of the attack lifecycle.
The South Korean government recently uncovered a criminal syndicate that compromised over 90 organizations, exfiltrating 8.2 million records. The group’s mastermind, a 32-year-old former cybersecurity professional, utilized the ARTEX framework to conduct 38 distinct ransom operations, demanding upwards of $270,000 per victim.

Furthermore, the emergence of "Crime-as-a-Service" platforms such as APEX AI, MessiahGPT, and DarkGPT has commoditized these advanced capabilities. These tools allow even low-skilled threat actors to bypass traditional security perimeters by providing "plug-and-play" access to stolen session tokens and automated attack scripts.
Official Responses and Expert Analysis
Industry leaders and security analysts are unanimous in their assessment: the "door" remains the same, but the "lockpick" has become sentient.
"AI has increased the attackers’ workforce, but the work still consists of looking for unlocked doors," note researchers from TrendAI. "What has changed is the ability to try thousands of doors at once, adapt to the target country’s language, and continue without fatigue."
Rapid7’s 2026 Global Threat Landscape report reinforces this sentiment, emphasizing that AI is not necessarily creating "new" categories of exploitation, but is rather "industrializing" existing ones. By integrating agentic AI into offensive workflows, attackers can now conduct research, develop malware, and craft convincing social engineering lures at a scale that exceeds the defensive capabilities of human security operations centers (SOCs).
Microsoft, in its analysis of the Storm-0940 incidents, noted that the key threat is not just the sophistication of the AI, but the breadth of the target set. When an autonomous agent can handle the tedious, repetitive tasks of a brute-force attack or credential stuffing, the attacker can focus their human intelligence on the high-value exploitation phase, significantly increasing the probability of a successful breach.
Implications: The Future of Defensive Posture
The implications of these developments are profound for organizations of all sizes. The traditional perimeter defense model is increasingly obsolete in the face of adversaries that operate with non-human speed and persistence.
1. The Death of Manual Defense
Organizations can no longer rely on manual threat hunting to keep pace with AI-driven attacks. Defenders must adopt "AI-vs-AI" strategies, where automated detection systems and autonomous response agents are deployed to counter the speed of machine-led incursions.

2. The Expansion of the Attack Surface
AI has fundamentally altered the attack surface. It is no longer just about software vulnerabilities; it is about the security of AI models themselves, the inference services they provide, and the session tokens that grant them access to cloud environments. Protecting the "AI supply chain" is now as critical as patching operating systems.
3. Localization and Precision
The ability of AI to generate perfect, native-language phishing campaigns means that localized threats will increase in frequency and effectiveness. Organizations must move beyond basic security awareness training and invest in behavioral analytics that can detect subtle deviations from normal user activity, regardless of how well-crafted the fraudulent communications are.
4. The Need for Ecosystem Resilience
As Trend Micro notes, the advantage lies with those who possess "ecosystem depth." It is not merely about having a single advanced AI tool, but about how reliably and independently those capabilities can be sustained. For defenders, this means building resilient, integrated security architectures that minimize the "blast radius" of a potential compromise.
Conclusion
The incidents of 2026 demonstrate that we have entered a new era of digital conflict. The weaponization of tools like CyberStrikeAI and ARTEX is not just a passing trend; it is the early stage of a fundamental shift in how cybercrime is conducted.
As threat actors move toward fully autonomous, agentic workflows, the window of opportunity for defenders is closing. The only viable path forward is to match the attackers’ pace—not through sheer human effort, which is physically limited, but through the strategic, ethical, and aggressive adoption of defensive AI. The "unlocked doors" of the internet are being pushed open by digital hands that never tire, and the race to secure them has only just begun.

 Dwi Wanna
 Suro Senen
 Nana Muazin
 Pevita Pearce
 Nila Kartika Wati
