
 Asep Darmawan
By Swati Khandelwal | September 27, 2026
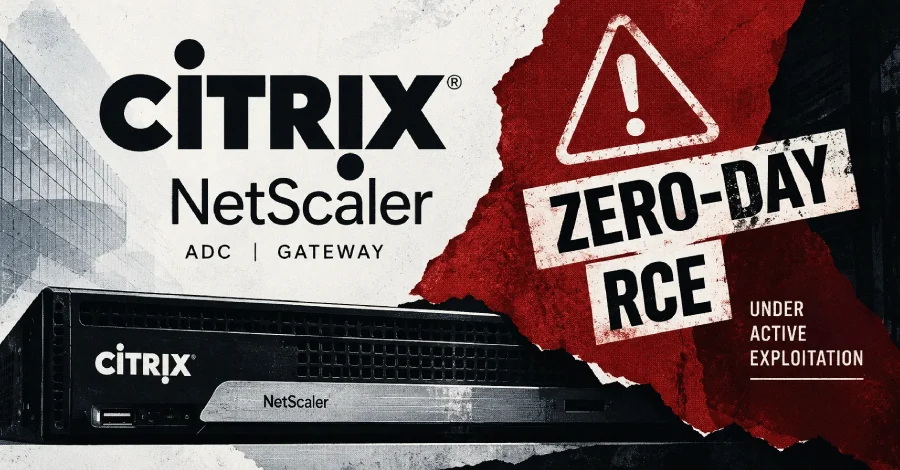
In a major escalation of network security threats, Citrix (a brand under the Cloud Software Group) has officially confirmed that two critical vulnerabilities impacting its NetScaler Application Delivery Controller (ADC) and NetScaler Gateway products are currently being exploited in the wild. The disclosure, issued on September 27, 2026, highlights the severe risks associated with edge-network infrastructure, where these devices serve as the critical gateway for VPNs, remote access, load balancing, and identity verification.
The security bulletin arrives following a wave of industry concern, including reports from security researchers and panicked IT administrators who were warned by suppliers to take their appliances offline preemptively. With the confirmation of active exploitation, organizations utilizing these platforms are now in a race against time to apply security patches and assess their environments for signs of unauthorized access.
The Core Vulnerabilities: A Technical Overview
The primary concern revolves around two remote code execution (RCE) flaws—tracked as CVE-2026-88771 and CVE-2026-88772. Unlike vulnerabilities that require specific misconfigurations, at least one of these flaws is inherent to the product’s architecture, affecting every deployment regardless of the specific configuration.
NetScaler ADC and Gateway devices reside at the "edge" of enterprise networks. Because they act as the gatekeepers for external traffic, they are prime targets for threat actors seeking a foothold within corporate environments. An RCE vulnerability in this context is catastrophic, as it allows an unauthenticated or low-privileged attacker to execute arbitrary code on the underlying appliance, potentially leading to full system takeover, lateral movement into internal segments, or the theft of sensitive session tokens and credentials.
Citrix has confirmed that these two flaws were exploited as zero-days—meaning they were being actively abused by malicious actors before a vendor-supplied patch was made available to the public.
Chronology of the Crisis
The timeline leading up to this disclosure highlights the rapid movement of modern threat actors and the critical importance of threat intelligence.

- September 25–26, 2026: Rumors began circulating among security researchers and enterprise IT teams regarding "several unpatched NetScaler RCE vulnerabilities."
- September 26, 2026 (Early): Security firm watchTowr publicly flagged that they were investigating credible reports of RCE exploits targeting NetScaler. They noted that their own forensic investigations confirmed the existence of at least two such vulnerabilities.
- September 26, 2026 (Mid-day): Panic erupted on forums like Reddit’s r/Citrix. Multiple administrators reported receiving urgent, "off-the-record" phone calls from their IT suppliers and security partners, advising them to disconnect their NetScaler appliances from the internet immediately to prevent compromise.
- September 27, 2026: Citrix officially broke its silence, issuing a security bulletin acknowledging the two exploited flaws. The company provided patches for these, alongside six additional, non-exploited vulnerabilities that were bundled into the release.
The speed at which the information moved from "rumors" to "emergency offline orders" suggests that the exploitation campaign was widespread and likely detected by multiple third-party security operations centers (SOCs) simultaneously.
Supporting Data and Affected Versions
The complexity of this situation is compounded by the fact that many organizations had only recently updated their systems to address a separate authentication bypass vulnerability (CVE-2026-19490) in August.
According to the official bulletin, appliances running versions 14.1-73.32 and 13.1-63.21—the very versions meant to secure the previous breach—are still vulnerable to the new RCE exploits. This puts a significant burden on IT teams who may have felt they were already "up to date."
The Patching Requirement
Citrix has urged customers to update their firmware immediately. Notably, the 13.1 branch had reached its "End of Maintenance" status on September 15, 2026. Despite this, the severity of the current exploits necessitated a release for that branch to protect the remaining user base. Organizations are advised to consult the official Citrix support portal to identify the exact build numbers required for their specific deployment.
The "Hidden" Six
In addition to the two critical RCEs, the update addresses six other vulnerabilities. While Citrix did not list these as currently exploited, the presence of multiple flaws in a single update cycle suggests a significant security audit was conducted on the codebase.
The Post-Compromise Reality: Patching is Not Enough
One of the most alarming aspects of this incident is the "persistence problem." Security experts, including the Netherlands’ National Cyber Security Centre (NCSC-NL), have warned in previous years—notably during the 2025 Citrix exploitation wave—that simply installing a patch does not automatically evict an attacker who has already gained a foothold.
If an attacker achieved RCE before the patch was applied, they likely established backdoors, created rogue administrative accounts, or injected persistent scripts into the system memory or storage.

Recommended Forensic Steps:
- System Integrity Check: Organizations must assume that any appliance exposed to the internet during the window of vulnerability (prior to the patch) may be compromised.
- Review Logs: Administrators should examine authentication logs, command history, and unexpected outbound network connections.
- Use Verification Scripts: While the NCSC-NL scripts from 2025 are dated, they serve as a template for identifying suspicious file modifications on NetScaler appliances.
- Credential Rotation: If an appliance is suspected of being compromised, all credentials, including VPN service account passwords and RADIUS secrets, must be rotated immediately. The appliance should be considered "burned" until a full wipe and re-image can be performed.
Implications for Enterprise Security
This incident serves as a stark reminder of the "Edge Security Paradox." By centralizing network services like VPNs and load balancing into a single appliance, enterprises gain efficiency but create a "single point of failure" that is highly attractive to nation-state actors and ransomware groups.
The Role of Threat Intelligence
The fact that watchTowr identified these flaws before the vendor’s public release highlights the growing gap between vendor disclosure and the reality of the threat landscape. Organizations that rely solely on vendor bulletins for their security posture are at a distinct disadvantage compared to those that monitor real-time threat intelligence feeds.
The "Go Dark" Strategy
The trend of administrators taking appliances offline at the first sign of a threat—even before a formal bulletin—is a sign of a maturing, albeit reactive, security culture. In the event of an RCE, the "business continuity" cost of shutting down a VPN for a few hours is significantly lower than the potential cost of a full-scale network breach, data exfiltration, or a ransomware deployment.
Official Response and Looking Ahead
As of the time of this writing, Cloud Software Group has not provided specific details regarding the threat actors behind these exploits or the scale of the campaign. The lack of documented indicators of compromise (IoCs) in the initial bulletin has left the defensive community to rely on community-shared intelligence.
The cybersecurity community remains on high alert. The combination of zero-day status, ease of remote exploitation, and the critical nature of the affected hardware makes this one of the most significant security events of the third quarter of 2026.
Advice to Administrators:
- Prioritize the patch: Apply the recommended updates immediately.
- Assume breach: If your appliance was online during the last 48 hours, treat it as compromised.
- Monitor outbound traffic: Watch for unusual data exfiltration patterns from your NetScaler management interfaces.
- Follow official channels: Monitor the Citrix Support Knowledge Center for additional guidance as more forensic data emerges.
The industry is watching closely to see if additional information regarding the threat actors—or more sophisticated exploitation techniques—surfaces in the coming days. For now, the priority remains the systematic identification and remediation of every NetScaler instance in the enterprise environment.

 Ali Ikhwan
 Jia Lissa
 Nila Kartika Wati
 Basiran
 Sagoh
 Lina Hope
