
Suro Senen
- Artificial Intelligence
- October 23, 2026
- 10 views
The PHP2Shell Crisis: When Embargoes Crumble in the Age of AI-Driven Exploitation
The recent disclosure of two critical, high-severity vulnerabilities in the PHP programming language—collectively dubbed "PHP2Shell"—has sent shockwaves through the global cybersecurity infrastructure. While the technical nature of the flaws (CVE-2026-109618…
Raul Delapena Setiawan
- Artificial Intelligence
- October 22, 2026
- 7 views
The Patch Apocalypse: Why AI-Driven Exploitation Has Outpaced Traditional IT Security
For decades, the rhythm of enterprise cybersecurity was dictated by a calendar. "Patch Tuesday" served as the heartbeat of IT operations—a predictable, albeit exhausting, cycle where security teams reviewed, tested,…
Siti Muinah
- Data Privacy and Ethics
- October 16, 2026
- 10 views
Critical RCE Flaw in Nextcloud’s Collabora App Fuels Exploitation Wave Amidst Disclosure Delays
In a stark reminder of the widening chasm between security patching and public transparency, threat actors have spent the last month exploiting a critical Remote Code Execution (RCE) vulnerability within…
Ali Ikhwan
- Data Privacy and Ethics
- October 14, 2026
- 12 views
Ivanti Under Fire: A Deep Dive Into the Latest Zero-Day Exploitation Crisis
The cybersecurity landscape has once again been shaken by a critical failure at the network edge. Ivanti, a staple provider of enterprise-grade security and IT management solutions, is currently grappling…
Rifan Muazin
- Data Privacy and Ethics
- October 10, 2026
- 19 views
Critical Security Alert: Citrix NetScaler Vulnerability CVE-2026-88779 Under Active Exploitation
In a significant development for enterprise cybersecurity, Citrix has issued an urgent advisory regarding a high-severity memory overflow vulnerability affecting its widely deployed NetScaler ADC and NetScaler Gateway appliances. The…
Asro
- Data Privacy and Ethics
- June 5, 2026
- 71 views
Critical Remote Code Execution Vulnerability in Everest Forms Pro Triggers Widespread Exploitation
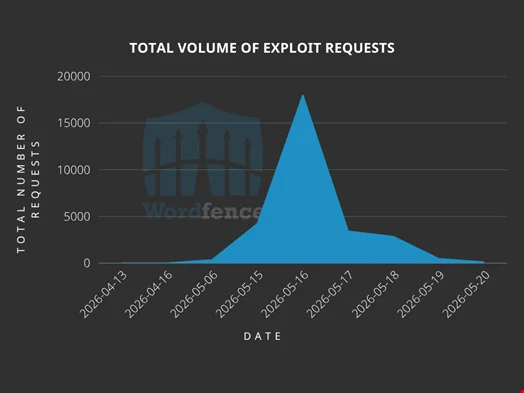
A high-severity security crisis is currently unfolding within the WordPress ecosystem as threat actors actively exploit a critical vulnerability in the Everest Forms Pro plugin. This flaw, which grants unauthenticated…
Nana Muazin
- Data Privacy and Ethics
- May 14, 2026
- 70 views
Critical Exim Mail Server Vulnerability: The Convergence of AI-Driven Exploitation and Open-Source Security
A newly discovered critical vulnerability in the widely deployed Exim mail transfer agent (MTA) has sent shockwaves through the cybersecurity community. Identified as CVE-2026-45185, this remote code execution (RCE) flaw…


 Reynand Wu

 Sagoh


 Azzam Bilal Chamdy

Beyond the Transaction: How to Transform Your Email List Into a Thriving Community
- October 24, 2026
- 1 views
