
 Siti Muinah
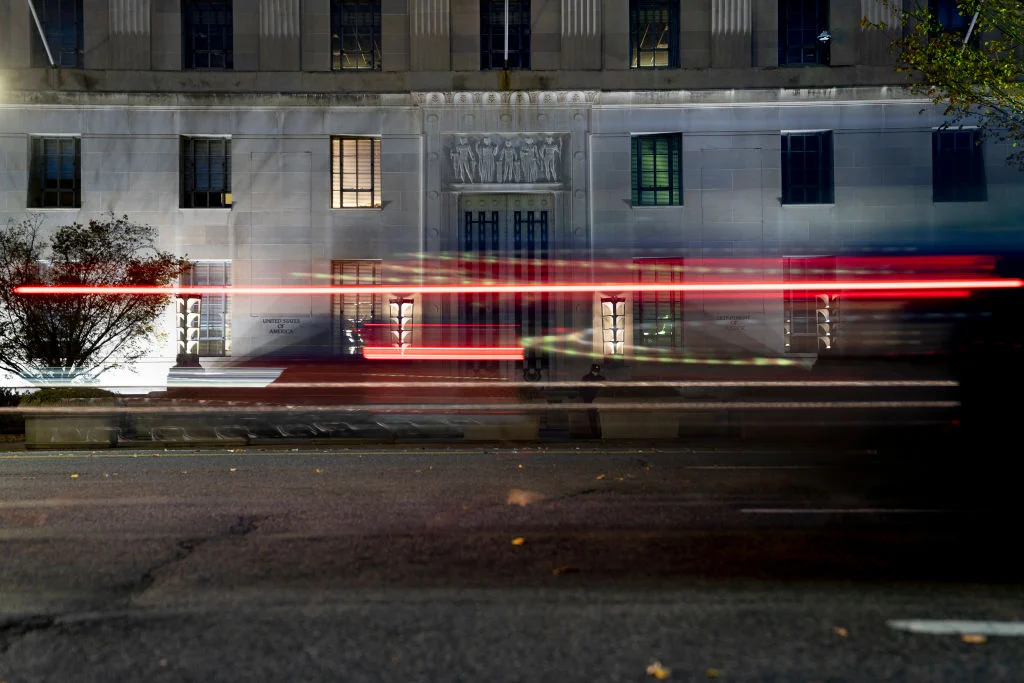
In a chilling case that underscores the vulnerabilities of military personnel to transnational cybercrime, Robert Wayne Boling Jr., 45, has pleaded guilty to orchestrating a sophisticated, years-long identity theft scheme. Operating from the shadows of the Philippines, Boling systematically targeted thousands of U.S. servicemembers and veterans, stripping them of their hard-earned benefits and personal financial security. The guilty plea, announced by the U.S. Department of Justice (DOJ) on Tuesday, marks the culmination of a grueling, years-long international manhunt to bring the primary architect of this fraud to justice.
Boling, who faces a maximum sentence of 40 years in federal prison, admitted to conspiracy to commit wire fraud and money laundering. His conviction serves as a grim reminder of how sensitive military data, when compromised, can be weaponized against the very people tasked with defending the nation.
The Architecture of the Fraud: How the Scheme Unfolded
The operation, which spanned from 2014 to 2019, was characterized by its cold-blooded efficiency. Prosecutors allege that Boling was not merely a participant but the “principal orchestrator” of the illicit enterprise. The fraud relied on a steady pipeline of Personally Identifiable Information (PII) harvested from the deepest levels of the military bureaucracy.
The breach began with Frederick Brown, a former Army contractor serving as a medical records administrator in South Korea between 2010 and 2015. Using his authorized access, Brown systematically exfiltrated the sensitive data of thousands of service members—including names, social security numbers, and private medical records. This data was then funneled to Boling, who used it to gain unauthorized access to bank accounts, Department of Veterans Affairs (VA) portals, and other financial institutions.
Once inside these accounts, Boling and his network of co-conspirators executed a series of unauthorized withdrawals and fund transfers. To move the money, the crew employed a sophisticated network of "money mules" across the United States. These individuals were recruited to provide bank accounts for the deposit of stolen funds, which were then laundered through various channels before being sent to Boling in the Philippines.
A Chronology of Deceit and Justice
The collapse of this criminal ring was not an overnight success but the result of a coordinated effort by federal investigators spanning nearly a decade.
- 2010–2015: Frederick Brown, a medical records administrator, abuses his position in South Korea to harvest the PII of thousands of U.S. military-affiliated individuals.
- 2014–2019: The peak of the fraud scheme. Boling orchestrates the theft of funds from bank accounts and VA benefits, utilizing a network of domestic money mules.
- July 2019: The initial indictment is unsealed. Boling is formally charged alongside four co-conspirators.
- 2020–2021: Two major co-conspirators, Trorice Crawford and Frederick Brown, are sentenced to 46 months and 151 months in prison, respectively.
- October 2022: A federal arrest warrant is issued for Boling, who remains at large in the Philippines.
- May 2026: Following extensive diplomatic and legal coordination, Philippine authorities deport Boling to the United States. He is arrested upon arrival in Los Angeles.
- September 2026: Boling enters a formal guilty plea in federal court, acknowledging his role as the mastermind of the operation.
Despite this progress, the case remains partially open. Two alleged co-conspirators, Jongmin Seok and Allan Albert Kerr, remain at large, continuing to be the subjects of an international search.
Quantifying the Impact: The Cost of Stolen Service
The human cost of this scheme is staggering. By targeting the accounts of elderly and disabled veterans, the conspirators did more than just steal currency; they compromised the stability of families who rely on military benefits for housing, healthcare, and daily sustenance.
The scope of the breach was wide-reaching, affecting thousands of individuals across the U.S. armed forces. Prosecutors have emphasized that the perpetrators showed no discretion, selecting victims based solely on the availability of their data. For many victims, the discovery of the fraud came as a devastating surprise, leading to months, or even years, of credit repair and legal battles to reclaim stolen benefits.
The financial data underscores the professional nature of the operation. By laundering money through multiple jurisdictions and utilizing dozens of U.S.-based intermediaries, the crew attempted to create a paper trail so complex that it would stymie federal investigators. However, the persistence of the DOJ’s Criminal Division eventually allowed authorities to map the flow of funds and identify the domestic mules who facilitated the movement of stolen capital.
Official Responses: A Commitment to Protecting Those Who Serve
The Department of Justice has framed this case as a moral imperative. In his official statement, A. Tysen Duva, assistant attorney general of the DOJ’s Criminal Division, condemned the betrayal inherent in the crime.
“Those who courageously served our nation deserve our gratitude and protection—not to become targets for criminals seeking to profit from their sacrifice,” Duva stated. “This defendant betrayed our country by exploiting personal information belonging to thousands of military-affiliated individuals… in a calculated scheme to steal from those who have given so much.”
Justin R. Simmons, the U.S. Attorney for the Western District of Texas, echoed this sentiment, underscoring the government’s resolve. “We will always work tirelessly to fully prosecute those who prey on others in this manner, especially when the victims of those crimes are servicemembers.”
The rhetoric from the DOJ signals a broader shift in federal strategy. As identity theft becomes increasingly globalized, the government is demonstrating a willingness to leverage international treaties and extradition agreements to pursue criminals who believe they can hide behind foreign borders.
Implications for Military Cybersecurity
The case of Robert Wayne Boling Jr. highlights a critical vulnerability in the U.S. military’s digital infrastructure: the "insider threat." While the Department of Defense (DoD) has spent billions on hardening its perimeter defenses against external hacking groups and foreign state actors, this case proves that the most dangerous threats can originate from within.
The Insider Threat Problem
The fact that Frederick Brown, a contractor, was able to extract massive amounts of PII over a five-year period suggests a failure in oversight and data compartmentalization. In the years since the 2015 conclusion of the breach, the DoD has shifted toward "Zero Trust" architectures—a framework where no user, regardless of their clearance or position, is inherently trusted. Under this model, access to sensitive databases is restricted, logged, and audited in real-time.
The Challenge of Transnational Prosecution
Boling’s residence in the Philippines highlights the legal hurdles of international cybercrime. The time elapsed between his indictment in 2019 and his arrest in 2026 illustrates how jurisdictional complexities can be exploited by criminals to delay justice. The successful deportation of Boling is a testament to the strengthening of international cyber-cooperation between the U.S. and Southeast Asian nations.
Protecting Future Benefits
The targeting of VA benefits suggests that government disbursement platforms remain high-value targets. As the VA continues to modernize its digital systems, it must balance ease of access for veterans with rigorous identity verification protocols. The integration of multi-factor authentication and biometric verification is becoming the new standard to ensure that only the rightful beneficiaries can access these accounts.
Conclusion
The conviction of Robert Wayne Boling Jr. is a victory for the thousands of servicemembers who were victimized by his greed. While the legal proceedings move toward sentencing, the case serves as a permanent mark on the history of military-related fraud. It provides a sobering lesson for both the government and the private sector: in an era of digital warfare, PII is a weapon. Protecting the privacy of those who wear the uniform is not just a matter of cybersecurity policy—it is a core component of the nation’s duty to its protectors. As the investigation into the remaining fugitives continues, the government’s message remains clear: there is no corner of the globe far enough to escape the reach of American justice.

 Raul Delapena Setiawan
 Lina Irawan

 Ammar Sabilarrohman

 Asep Darmawan

 Asro

 Layla Zulfa

 Nila Kartika Wati

 Muslim
