
 Sagoh
By Cybersecurity Investigative Desk
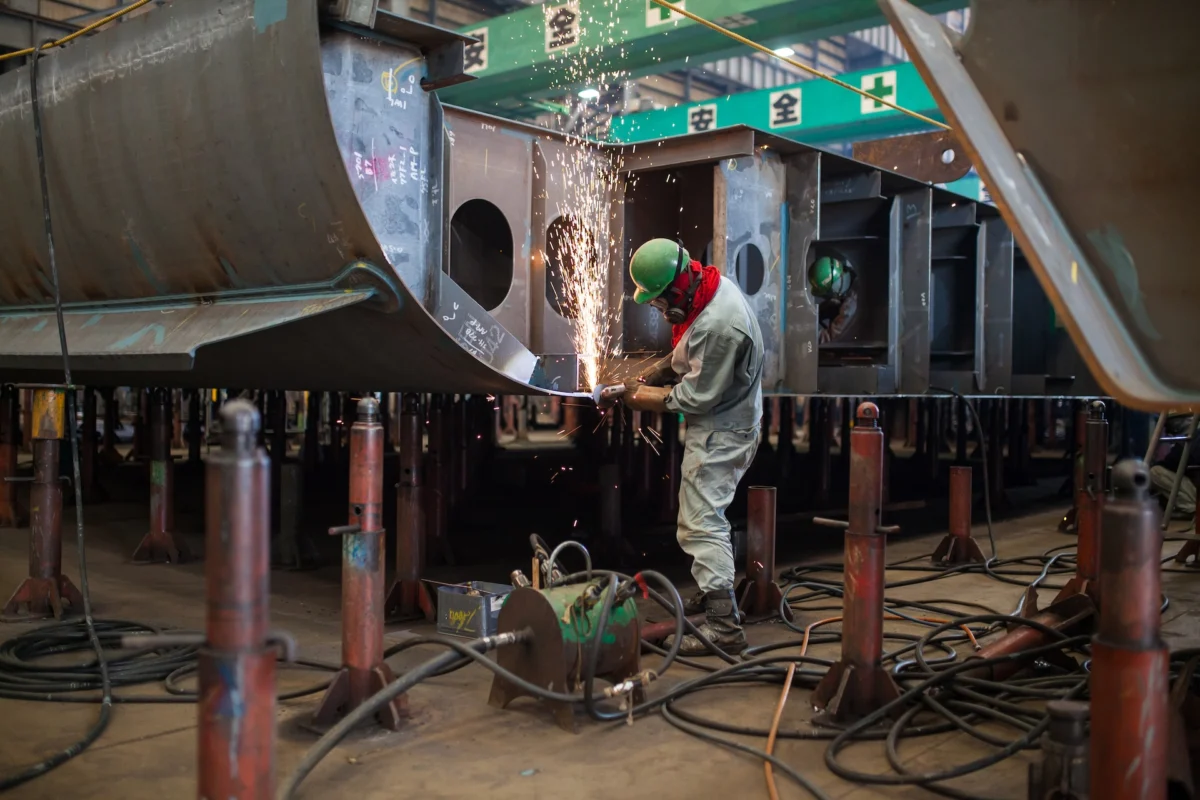
A sophisticated, state-sponsored cyber-espionage campaign has set its sights on critical NATO defense infrastructure, according to a report released Tuesday by the Symantec Threat Hunter Team. The campaign, which has targeted naval shipbuilders, military aircraft engine manufacturers, and national law enforcement agencies, has been attributed to the notorious Russian threat actor known as "Forest Blizzard"—also recognized in the intelligence community as APT28, Fancy Bear, and Swallowtail.
This group, which carries a long history of high-profile operations including the 2016 interference in the U.S. presidential election, is widely understood to be an arm of the Russian GRU (Main Intelligence Directorate). The discovery of this new campaign underscores the ongoing, high-stakes "shadow war" occurring in cyberspace as the conflict in Ukraine continues to evolve.
Main Facts: A Targeted Offensive
Symantec researchers discovered that the hackers were not conducting random, opportunistic attacks. Instead, the campaign displayed the hallmarks of a highly disciplined, intelligence-gathering operation. By targeting specific defense firms and law enforcement, the actors demonstrated a clear strategic intent: to map out the logistical and technological capabilities of NATO-aligned nations.
A central element of the intrusion was the use of "hands-on-keyboard" activity. Unlike automated malware, which executes a predetermined set of instructions, this technique involves human operators actively navigating a compromised network in real-time.
"Hands-on-keyboard activity means a human operator is choosing what to do next," said Dick O’Brien, principal intelligence analyst at the Symantec Threat Hunter Team. "It’s essentially confirmation that the organization is a genuine target for the operators, not an accidental infection. It also confirms that further exploitation beyond the initial infection was at least attempted."
In one notable instance, hackers repeatedly accessed a compromised naval shipbuilder’s host over the course of a full week, methodically exfiltrating sensitive credentialed material before their presence was identified.
Chronology of the Threat
The evolution of this specific campaign follows a timeline that suggests an escalating effort by Russian intelligence to monitor Western military support for Ukraine.
- September 2023: Recorded Future’s Insikt Group first identifies attacks on defense and diplomatic targets across Romania, Spain, and Turkey. These attacks utilized the "Hookedge" backdoor, a malicious tool that would eventually become a signature of this broader campaign.
- August 2024: The Hookedge backdoor is officially documented by security researchers, revealing its role in facilitating persistent access for Russian actors.
- Spring 2025: Western government agencies and cybersecurity partners successfully disrupt a major Forest Blizzard espionage campaign, leading to a temporary lull in activity and a shift in the group’s infrastructure.
- Recent Months (2026): Symantec observes a new surge in activity. The group pivots to more advanced, undocumented loaders and dedicated command-and-control servers, signaling a refinement of their tactics to evade detection by Western security firms.
Supporting Data and Technical Analysis
The technical sophistication of this campaign highlights the GRU’s ability to adapt when its existing toolsets are exposed. When the Hookedge backdoor became known to the cybersecurity community, the actors did not abandon the effort; they evolved their methodology.
The "ld.exe" Loader
One of the most alarming aspects of the recent findings is the deployment of a previously undocumented loader, identified by the filename ld.exe. This tool serves as a gateway for more malicious payloads, yet it is uniquely designed to frustrate security analysts.
According to O’Brien, the loader performs its decryption in memory rather than on the disk. Crucially, it requires a unique key supplied at runtime via the command line. "Without both the encrypted file and the key, the payload can’t be recovered," O’Brien noted. "We didn’t recover it, so we don’t know its function."
Infrastructure Shifts
While security researchers initially anticipated that the group would continue to "hop" between free hosting services—a common tactic for low-level cybercriminals—these actors did the opposite. They transitioned their most sensitive activity to dedicated servers. This move is indicative of a well-funded, state-backed entity that has the resources to manage its own infrastructure rather than relying on compromised third-party platforms.
Official Responses and Strategic Context
The Biden administration and its NATO counterparts have been increasingly vocal about the risks posed by Russian state-sponsored actors. In recent years, the FBI and CISA have taken aggressive measures to dismantle GRU-linked botnets and infrastructure.
However, these tactical "takedowns" are often viewed as temporary setbacks for a group as entrenched as Forest Blizzard. The intelligence community remains concerned that the motive for these specific attacks—beyond general espionage—is to gain actionable intelligence on the supply chain of weapons and logistics provided to Ukraine. By compromising the manufacturers of ship engines and naval vessels, the hackers are essentially gaining a blueprint of the military hardware being deployed or maintained in the region.
"This is clearly a campaign aimed at intelligence collection regarding Western government and defense targets," O’Brien stated. "The timing and the targets suggest a direct link to the ongoing geopolitical friction between Russia and the nations actively supporting the Ukrainian war effort."
Implications for Global Security
The implications of this campaign are far-reaching, affecting both private industry and national security.
1. The Vulnerability of Defense Contractors
Defense contractors, particularly those in the maritime and aerospace sectors, are currently the "front line" of cyber warfare. Because they possess proprietary data that is critical to national defense, they are high-value targets. This incident serves as a stark reminder that even robust cybersecurity measures can be bypassed by human-operated, persistent threats.
2. Escalation of Cyber-Espionage
The transition to memory-only payloads and custom-built, undocumented loaders shows that Russian hackers are prioritizing "stealth" above all else. This evolution makes it significantly harder for Endpoint Detection and Response (EDR) systems to trigger alerts, as the malicious code never touches the hard drive in an unencrypted state.
3. Geopolitical Alignment
The geographic distribution of the targets—specifically NATO member nations—is not coincidental. It signals that the Russian military is attempting to gather as much intelligence as possible on how the West is coordinating its military support. Any information gained by the GRU could potentially be used to sabotage supply lines, disrupt manufacturing, or inform Russian tactical decisions on the battlefield in Ukraine.
4. A Call for Enhanced Vigilance
For organizations in the defense sector, the advice from cybersecurity experts is clear: perimeter defense is no longer sufficient. Companies must implement strict "zero-trust" architectures, monitor for anomalous "hands-on-keyboard" behavior, and ensure that their incident response teams are prepared for sophisticated, human-driven attacks that do not rely on standard, signature-based malware.
As the conflict in Europe shows no signs of abating, the digital battleground is becoming increasingly crowded. The activities of groups like Forest Blizzard suggest that for state-sponsored actors, the war is not just fought with missiles and tanks, but through the silent, persistent infiltration of the systems that power the modern defense industrial base.
For now, the international community remains on high alert. As Symantec and other firms continue to analyze the remnants of this campaign, the focus shifts to how these private sector discoveries can be translated into actionable intelligence for government agencies, and whether such revelations will lead to further diplomatic repercussions against the Russian state.

 Raul Delapena Setiawan
 Evan Lee Salim
 Jia Lissa
 Neng Nana
 Rifan Muazin
