 Evan Lee Salim
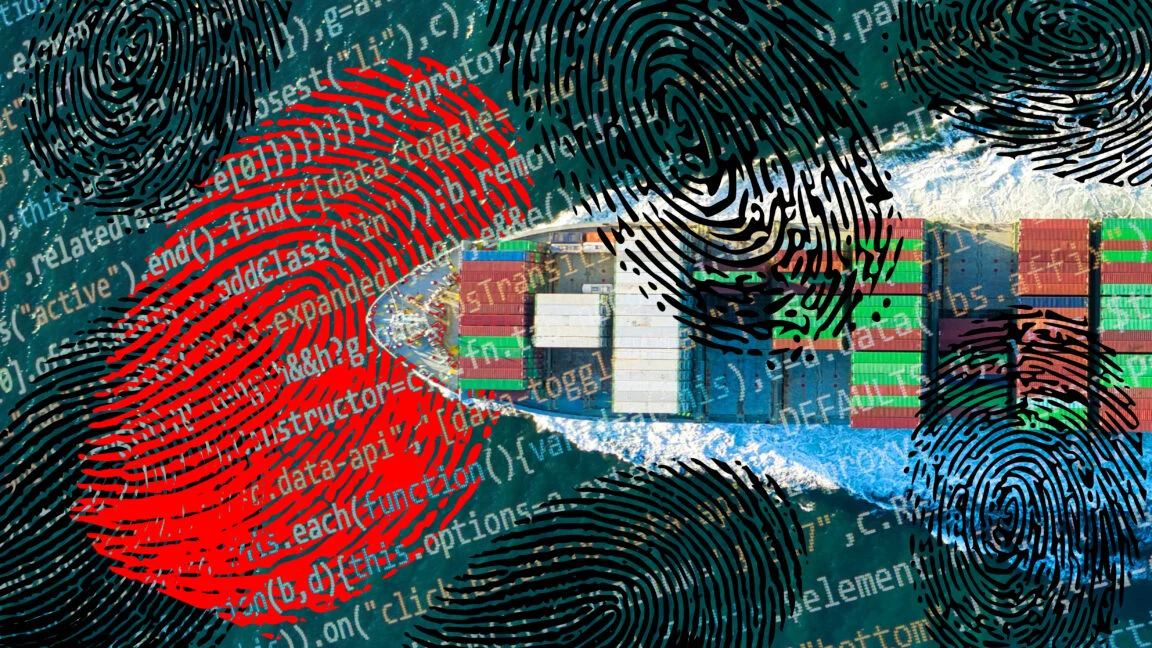
In a landmark victory for modern cybersecurity, Google’s Threat Intelligence Group has pulled back the curtain on a covert, months-long operation that allowed the tech giant to peer into the inner workings of TeamPCP, a notorious hacker collective responsible for one of the most destructive software supply-chain campaigns ever recorded.
Before the arrests of two key figures in Australia last month, TeamPCP had successfully compromised hundreds of open-source projects, hijacked developer credentials, and deployed a self-spreading, Dune-inspired worm known as "Mini Shai-Hulud." The group’s activities, which breached over a thousand companies, represented a sophisticated evolution of cyber-warfare. However, as the hackers celebrated their exploits in private, encrypted channels, they were unaware that a Google-controlled persona was sitting in the same virtual room, documenting their every move.
The Anatomy of a Digital Infiltration
The revelation, detailed by Google Threat Intelligence researcher Austin Larsen at the SentinelOne LABScon conference, marks a paradigm shift in how private industry handles active cyber threats. Rather than merely reacting to breaches after the fact, Google’s Mandiant security subsidiary embedded an undercover analyst within the group’s "CanisterWorm" core chat server as early as March 2026.
According to Larsen, the process of infiltrating TeamPCP was a long-game strategy that relied on patience and social engineering. "One of our personas had been working for many months to build trust with one of the actors that was invited to join TeamPCP," Larsen explained. "Essentially, almost day one, Mandiant was watching everything behind the scenes."
This "fly on the wall" approach did not involve active participation in criminal acts. Instead, the undercover analyst maintained a low profile, gathering intelligence while the hackers boasted about their accomplishments. At one point in the leaked chats, a TeamPCP member audaciously declared, "You guys should understand that we pulled off the biggest supply-chain [attack] maybe ever recorded in modern history."
Chronology of the Rampage and Disruption
The rise and fall of TeamPCP followed a chaotic, high-velocity timeline that fundamentally challenged the security of the global software ecosystem.
Phase 1: The Initial Breach (Early 2026)
TeamPCP emerged in late 2025, quickly pivoting to a strategy of poisoning open-source repositories. By spring 2026, the group had successfully compromised high-profile tools, including the security scanner Trivy, the AI API tool LiteLLM, the web app library TanStack, and infrastructure belonging to Checkmarx and Mistral AI. These initial footholds provided the leverage needed to compromise larger entities, including GitHub, the data firm Mercor, and individual employee devices at OpenAI and the European Commission.

Phase 2: The "Mini Shai-Hulud" Campaign
As the group scaled its operations, it turned to automation. The deployment of the "Mini Shai-Hulud" worm—named after the gargantuan sandworms of Frank Herbert’s Dune—allowed the hackers to automate the propagation of their malware. This worm scanned for vulnerabilities and planted malicious payloads with terrifying speed, forcing security teams worldwide into a reactive scramble.
Phase 3: The Inside Pivot
By March, Google’s analyst had successfully gained access to the group’s "CanisterWorm" channel, where the hackers stored stolen credentials. Realizing the potential for a massive extortion scheme, Google’s team shifted from observation to disruption. Rather than alerting individual victims, which would have been too slow to stem the tide, Google contacted service providers like Microsoft and Amazon Web Services. They provided lists of compromised access tokens and credentials, enabling providers to revoke them instantly before the hackers could exploit them.
Phase 4: The Internal Collapse (Summer 2026)
The downfall of TeamPCP was accelerated by the group’s own greed and poor operational security (opsec). Struggling to monetize their vast trove of over half a million stolen credentials, the group partnered with the infamous cybercriminal gang "ShinyHunters." The partnership was short-lived. In April, ShinyHunters betrayed their partners, going rogue and conducting their own extortions using the stolen data. In an act of pure irony, ShinyHunters sent logs of the internal TeamPCP chats to Google’s researchers, unaware that Google already had direct access to the source.
The Trail of Breadcrumbs: Identifying the Perpetrators
The arrest of two Australians—Ruben Ian Thomson and Louis Michael Gaebler—in late August 2026 was the direct result of a collision between sophisticated state-level intelligence and elementary human error.
Larsen’s investigative process was meticulous. By analyzing data leaked from the BreachForums hacker site, he linked a persistent, high-activity handle in the CanisterWorm chat to a Gmail address: [email protected]. Cross-referencing this with archived forum disputes revealed a 2019 transaction involving a PayPal account tied to [email protected].
The final nail in the coffin was the group’s decision to move their stolen data to a new server, which they inexplicably backed up to a Google Drive account associated with the same [email protected] address. When Google researchers discovered that the hackers were hosting illicit material on their own platform, they handed the evidence to the FBI. The response from federal authorities was near-instantaneous.
The Role of AI in Emerging Threats
One of the most alarming aspects of the investigation was the discovery that TeamPCP members were utilizing AI to craft zero-day exploits. Google’s internal monitoring revealed that the hackers were leveraging AI tools to develop a novel method for bypassing multi-factor authentication (MFA) in widely used login software.
The undercover analyst managed to obtain the exploit code, which Google then verified and patched by alerting the software developer before the attack could be deployed in the wild. This incident serves as a stark reminder of the "dual-use" nature of AI: while it empowers developers, it simultaneously lowers the barrier to entry for cybercriminals looking to manufacture sophisticated, high-impact vulnerabilities.
Official Responses and Strategic Implications
The FBI has remained tight-lipped regarding the specifics of the ongoing prosecution, citing the sensitivity of active investigations. However, in a statement provided to WIRED, the agency emphasized its commitment to new, proactive cyber strategies. "The FBI is able to confirm we strive to increase impact on adversaries through partnerships as documented in our newly released FBI Cyber Strategy," the statement read.
For Google, this case represents the inaugural success of its newly formed "Cyber Disruption Unit." The unit is tasked with moving beyond the traditional role of "report and document" toward a more interventionist posture. As Larsen noted, "Writing reports can only be so useful. Taking action to protect users and customers—that is the next step."
Implications for the Future of Cybersecurity
The TeamPCP saga carries profound implications for the tech industry:
- The Fragility of the Supply Chain: The success of the hackers in moving from small open-source libraries to major enterprise platforms like GitHub and OpenAI underscores the systemic risk inherent in modern software development.
- The Power of Proactive Disruption: Google’s ability to coordinate with cloud service providers to revoke stolen credentials in bulk suggests a new model for incident response—one that relies on upstream intervention rather than individual cleanup.
- The Persistence of Human Error: Despite the use of sophisticated worms and AI-generated exploits, the hackers were undone by the most mundane of mistakes: re-using a personal email address for illicit activity.
- The Ethical Boundaries of Infiltration: While Google’s actions were lauded for their effectiveness, they raise complex questions regarding the ethics of corporate-led counter-hacking. Google was careful to state that its analyst remained a "fly on the wall," strictly avoiding the facilitation of illegal acts, a boundary that will likely become a major topic of debate as more tech firms adopt similar disruption tactics.
As the legal proceedings against Thomson and Gaebler move forward in Australia, the tech world is left to contend with a new reality. The era of passive defense is effectively over. In the shadow of the Dune-themed worm and the betrayal of the ShinyHunters, the lesson is clear: in the modern digital landscape, the most effective security tool is often an undercover seat at the table.

 Suro Senen
 Jia Lissa
 Lina Irawan
 Ammar Sabilarrohman
 Nana Wu