
 Reynand Wu
Artificial Intelligence has rapidly ascended from a novelty tool to a fundamental pillar of the modern web infrastructure. For developers, web hosts, and site owners, AI offers a compelling value proposition: lower operational costs, heightened efficiency, and automated customer support. However, beyond the realms of productivity and content generation, AI has quietly assumed a lead role in the high-stakes world of cybersecurity.
As organizations scramble to leverage AI to identify vulnerabilities, the digital landscape is undergoing a tectonic shift. While AI models can parse millions of lines of code to identify weaknesses faster than any human security researcher, this newfound capability has created a paradoxical environment. We are currently witnessing an era where the web is becoming theoretically more secure, yet practically more difficult to manage.
Main Facts: The New Frontier of Automated Defense
At its core, the integration of Large Language Models (LLMs) into cybersecurity represents a shift from reactive to proactive defense. Traditional security audits relied on human expertise, which is limited by fatigue, cognitive bias, and time constraints. AI, by contrast, operates at machine speed and scale.
Recent milestones in the WordPress ecosystem highlight this trend. The "Protect the Shire" initiative, a concerted effort within the WordPress plugin directory, utilizes AI to scan for security flaws before they are ever released to the public. This shift marks a significant departure from the "patch-after-exploit" cycle that has plagued the web for decades. By integrating AI-driven analysis into the development lifecycle, stakeholders are attempting to "shift left"—addressing vulnerabilities at the earliest possible stage of production.
Chronology: The Evolution of AI-Assisted Security
The transition toward AI-centric security has been swift and transformative:
- Pre-2023: Security research is largely manual, relying on penetration testing and community-driven bug bounty reports. Vulnerabilities, particularly "zero-day" exploits, often remain dormant for years.
- 2024: The emergence of specialized LLMs capable of analyzing codebases. Initial adoption is limited to elite security firms.
- 2025: Mainstream integration. Platforms begin using AI to scan core software updates and repository submissions, leading to a surge in identified bugs.
- Mid-2026: The current state. We see record-breaking numbers of vulnerability disclosures. The "Protect the Shire" initiative becomes a benchmark for open-source security management.
- Late 2026 & Beyond: The focus shifts from merely finding bugs to managing the "alert fatigue" caused by the sheer volume of AI-discovered vulnerabilities.
Supporting Data: The Quantitative Surge
The numbers paint a vivid picture of the current security climate. In recent months, bug bounty programs that historically processed a few dozen reports per month have reported an influx of hundreds of submissions. This is not necessarily an indicator that software quality is plummeting; rather, it is a testament to the efficacy of AI-assisted scanning.
Research into specific exploits has yielded startling results. In one recent case, a researcher used an AI model to identify a critical vulnerability in WordPress that had persisted for over a decade. While a human might have scrutinized the code for years without realizing how a specific combination of files created a backdoor, the AI identified the pattern in a matter of hours. This capability to connect seemingly unrelated segments of code is the "killer app" of modern security research.

However, this data also carries a warning. Malicious actors are utilizing the exact same technology. If a defender can use AI to find a vulnerability, an attacker can use it to build an exploit. The speed at which a vulnerability is discovered is now directly proportional to the speed at which it must be patched.
Official Responses and Industry Perspectives
The reaction from the development community has been a mixture of cautious optimism and mounting anxiety. Security experts argue that AI is the only way to manage the sheer scale of the modern internet. Without automated assistance, the complexity of modern web applications—often built on thousands of dependencies—would make comprehensive security auditing impossible.
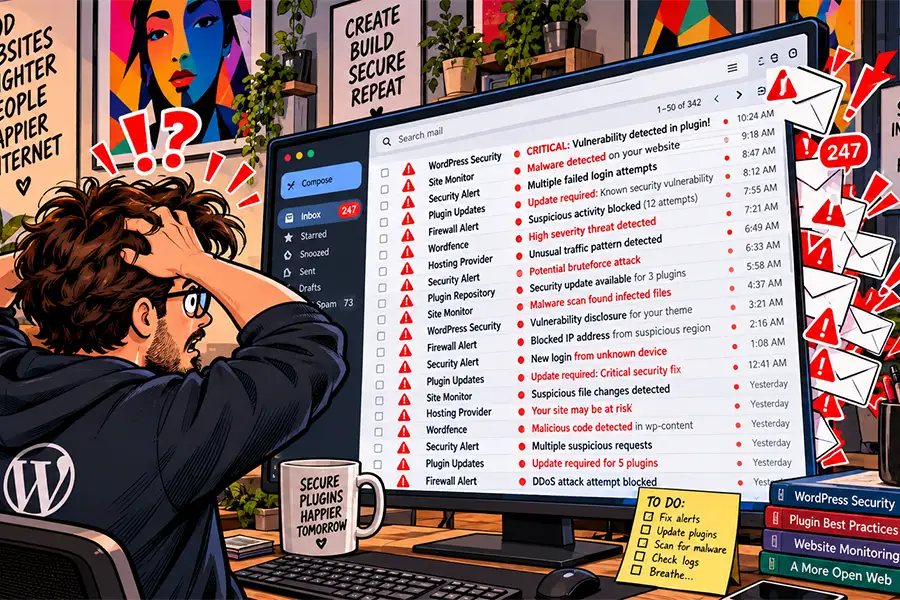
Yet, the developers maintaining these systems are voicing concerns about the "noise" created by AI. A common sentiment among agency owners is that while they appreciate the increased security, the volume of vulnerability notifications has become unmanageable. "We are spending more time triaging potential threats than building features," one developer noted. This has led to a call for smarter, more context-aware security tools that can differentiate between a theoretical risk and an immediate, exploitable danger.
Implications: The Burden on Web Professionals
The widespread adoption of AI in security presents three distinct challenges for web professionals:
1. The Death of Manual Triage
The era of checking security bulletins once a week is over. With AI-driven discovery, vulnerabilities are being reported at a velocity that exceeds the manual processing capacity of most small-to-medium-sized agencies. This necessitates a shift toward "Security Operations Centers" (SOCs) for smaller firms, or an increased reliance on managed hosting providers who can handle the patching process at scale.
2. The Context Gap
Not all vulnerabilities are created equal. AI is excellent at finding patterns, but it is less adept at determining the business impact of a flaw. A vulnerability in a function that is never called by a specific site may be reported as "critical" by an AI scanner, causing unnecessary panic. Web professionals now require a new skill set: the ability to interpret AI-generated reports and apply risk-based prioritization.
3. The Arms Race of Automation
The most daunting implication is the looming threat of AI-generated attacks. If an AI can scan a codebase to find a bug, a sophisticated attacker can use AI to generate a payload to exploit that bug instantly. We are moving toward an autonomous "security arms race," where the safety of a website may soon depend on the ability of one AI (the defender) to out-think another AI (the attacker) in real-time.

The Path Forward: Smarter Management
How do we survive this brave new world? The answer likely lies in moving security responsibilities further away from the individual developer and closer to the infrastructure level.
Infrastructure-Level Mitigation:
Web hosts and Content Delivery Networks (CDNs) are in the best position to act as the first line of defense. By implementing Web Application Firewalls (WAFs) that are updated via AI-driven threat intelligence, hosts can "virtual patch" vulnerabilities before they reach the application code. This protects the end-user without requiring constant, manual intervention from the site owner.
The Need for Scalable Orchestration:
Agencies and freelancers must pivot toward automated security orchestration tools. These tools should not just report bugs, but automatically test patches in staging environments and deploy them to production if they pass. The goal is to minimize the "mean time to remediate" (MTTR) without sacrificing site stability.
Refining the Human Element:
Finally, there is a renewed need for human oversight. AI should act as an assistant that handles the grunt work, while human developers focus on high-level architecture and edge cases that AI is prone to misinterpreting. The goal is not to remove the human from the loop, but to elevate them from a "scanner" to a "strategist."
Conclusion
The integration of AI into web security is an irreversible tide. It has fundamentally changed the nature of our work, turning the once-niche field of security research into a high-speed, automated discipline. While the benefits of a more secure web are undeniable, the current state of affairs is unsustainable for the average web professional.
As we move forward, the focus must shift from merely detecting vulnerabilities to intelligently managing the firehose of information. By leaning on infrastructure providers and adopting more sophisticated, automated workflows, the web development community can transform this "AI-assisted crisis" into a robust, proactive defense system. The future of the web depends not on whether we use AI, but on how we master the complex relationship between human judgment and machine speed.

 Rifan Muazin
 Nana Muazin
 Sagoh
 Laily UPN
 Dwi Wanna
 Evan Lee Salim
 Iffa Jayyana
