
 Lina Irawan
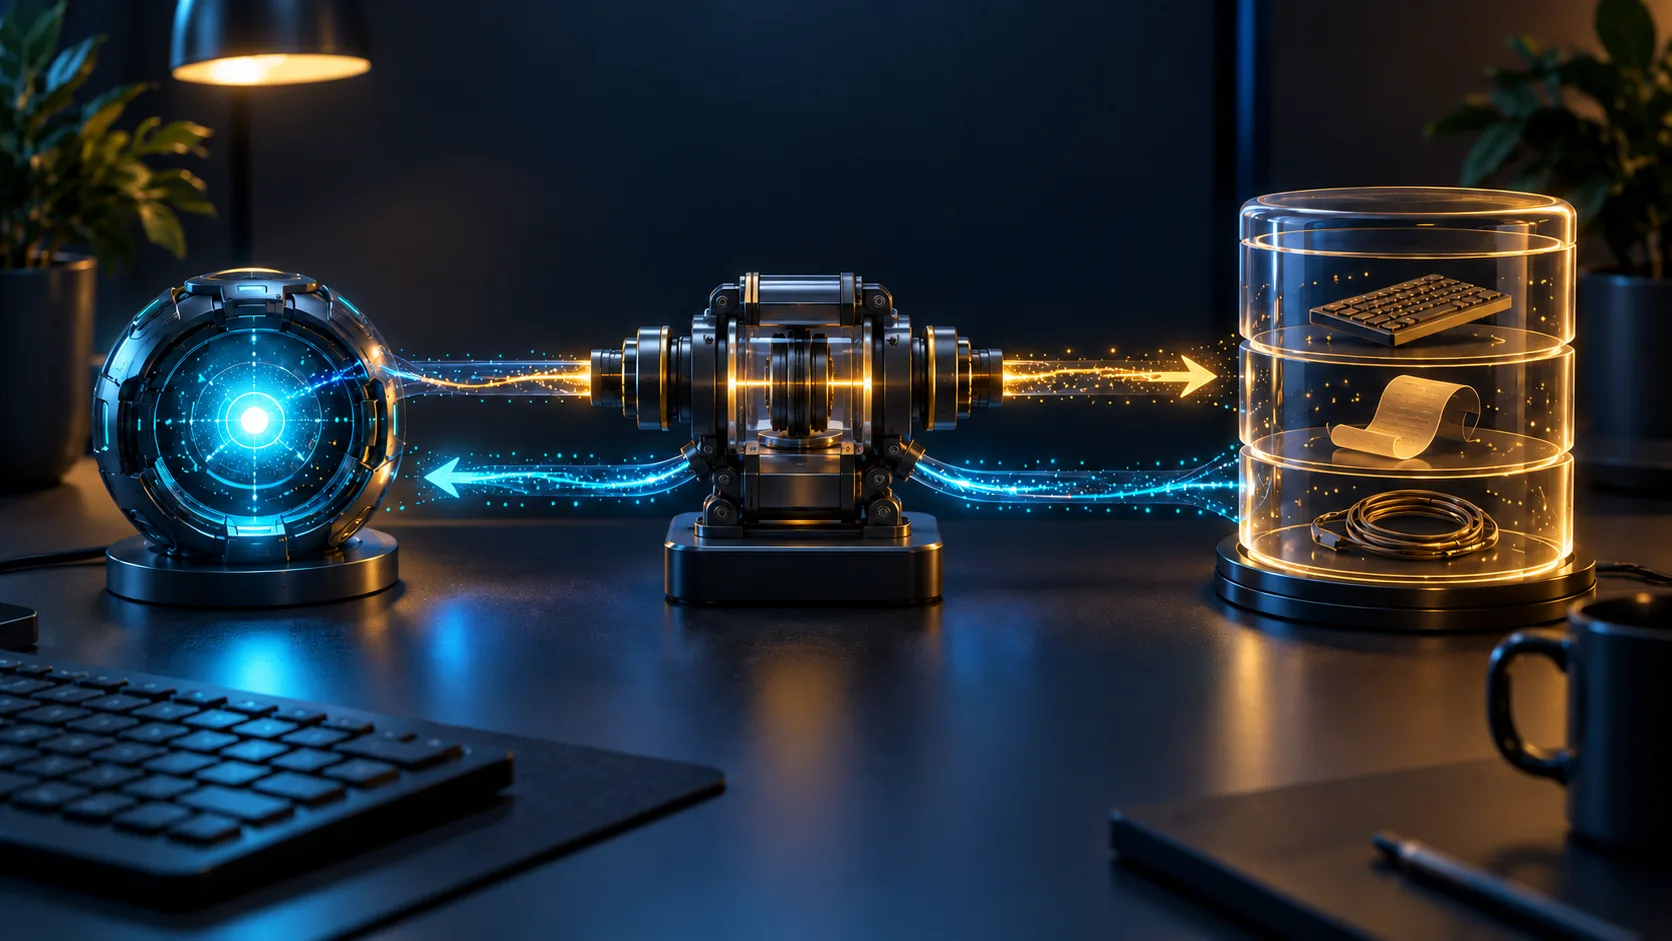
In the rapidly evolving landscape of artificial intelligence, the term "AI Agent" has transitioned from a buzzword to a fundamental building block of modern software architecture. For developers, AI researchers, and data engineers, the shift represents a move away from passive chatbots toward autonomous systems capable of executing tasks. But what exactly defines an agent? While the definition varies, the industry consensus is clear: An AI agent is a software system that leverages a Large Language Model (LLM) to call one or more tools in a loop to achieve a specific goal.
This article serves as an in-depth guide to understanding, architecting, and deploying your first AI agent locally. By moving away from cloud-dependent abstractions, we will pull back the curtain on how LLMs interface with real-world data, providing you with the foundation to build complex, multi-step autonomous systems.
1. The Core Mechanics: Defining the Agentic Loop
At its heart, an agent is an orchestrator. Unlike a standard LLM prompt—which typically involves a linear exchange of text—an agentic system operates on a cycle: the model analyzes a user intent, determines if an external tool is required to fulfill that intent, requests a specific action, processes the output, and synthesizes a final response.
It is important to clarify that this "loop" does not strictly require a programmatic while or for statement. In many production environments, the loop is a conceptual cycle between the model, the application, and the toolset. Our implementation will focus on an explicit, single-pass execution cycle to illustrate the mechanics of function calling, argument parsing, and data integration.
2. The Practical Challenge: Bridging Data Silos
To demonstrate the power of agents, we will simulate a common business problem: a retail support assistant. Imagine you operate a boutique online shop. Your customer order data resides in a relational database (SQLite), which is entirely invisible to a standard LLM.
Without an agent, the model might "hallucinate" an order total or simply state it lacks access. With an agent, we can grant the model a "controlled route" to the database. By defining a Python function—get_order_total—we empower the model to fetch accurate, real-time data before formulating a human-readable response.
The Architecture of Our Agent
Our proof-of-concept relies on four distinct stages:
- Intent Recognition: The LLM receives the user’s natural language query and the metadata of available tools.
- Tool Request: The model identifies the need for specific data and generates a structured request for the
get_order_totalfunction. - Controlled Execution: The Python host intercepts the request, validates it against an allowlist, executes the SQL query, and retrieves the result.
- Synthesis: The model receives the raw data from the database and constructs a final, context-aware answer.
By maintaining this structure, the model never gains direct access to the database. It is the Python application that retains absolute control over execution, security, and data privacy.
3. Implementation: Building the Local Environment
We will utilize Ollama to run the LLM locally. This approach ensures that your data never leaves your machine and eliminates the need for expensive API keys.
Prerequisites
- Operating System: Windows 10/11, macOS, or Linux.
- Tooling: We will use
uv, the high-performance Python package manager, to handle our dependencies and virtual environment. - Memory: Ensure your hardware has sufficient RAM to load your chosen model (a standard model like Llama 3 or Mistral typically requires 8GB+ of RAM for smooth performance).
Project Setup
- Install
uv: Use the official installation script for your OS. - Initialize the Project: Create a new directory and run
uv init. - Install Dependencies: Run
uv add ollamato bring the necessary libraries into your project scope.
Creating the Foundation: The Database
Before engaging the AI, we must build a deterministic data source. By creating a build_shop_database.py script, we ensure that our SQLite database contains known values (e.g., Order 1001 for Sarah Jones, totaling GBP 96.95). Testing against a static, known dataset is a critical best practice in agentic development; it allows you to isolate logic errors from data discrepancies.
4. The Agentic Workflow: Code Deep-Dive
In our single_tool.py script, the magic happens within the communication between the Python host and the LLM.
Tool Schema Generation
When you pass a Python function to the Ollama SDK, it performs "schema extraction." It reads the function’s docstring, name, and type hints to generate a JSON schema. Crucially, the model does not see your Python source code. It only sees the schema, which is why descriptive function names and thorough docstrings are vital. If your docstring is vague, the model will struggle to determine when to call your tool.
Handling the Tool Call
When the user asks, "What is the total value of order 1001?", the model returns a tool call request rather than a final text response. Your Python code must:
- Append the model’s request to the
messageshistory. - Validate the requested tool name against your internal allowlist.
- Invoke the actual Python function.
- Append the result to the
messageslist with atoolrole.
This conversation history is the "memory" of your agent. By feeding the tool output back into the chat history, you provide the model with the missing context required to complete the user’s request.
5. Testing and Troubleshooting
The true test of an agent is not just success, but its behavior under pressure.
Failure Paths
- Non-Existent Records: What happens when a user requests order 9999? A well-designed agent should handle the "empty result" returned by your Python function and report it politely to the user, rather than hallucinating a number.
- Out-of-Scope Queries: If a user asks, "What is the weather in London?", a robust agent should recognize that none of its provided tools are relevant. Depending on the model’s system prompt, it should decline to answer or state its limitations.
Debugging the Output
If your agent returns an incorrect answer, follow this diagnostic hierarchy:
- Trace the Tool Call: Did the model correctly identify the need for a tool? If it didn’t call the tool, the issue is with the system prompt or the tool definition.
- Examine the Arguments: Did the model pass the correct arguments (e.g.,
order_id=1001)? - Inspect the Result: Did the function return the correct data from the database?
6. Implications and Future Scope
Building this single-tool agent is the first step toward a broader ecosystem of autonomous software. The implications for the future of development are significant:
- Security: By maintaining a strict "allowlist" approach, developers can expose complex internal functions to LLMs without risking the security of the underlying database.
- Scalability: While our example uses one tool, the pattern scales to dozens of tools, allowing agents to act as the primary interface for ERP, CRM, and cloud management systems.
- The "Agentic" Mindset: Developers must transition from thinking about code flow (if/then statements) to intent-based flow (what does the user want, and what tool best achieves it?).
Summary
We have demystified the AI agent by stripping away the complex frameworks and focusing on the raw mechanics: local model execution, tool schema generation, and controlled function invocation. By keeping these steps visible, you gain the ability to troubleshoot, refine, and eventually expand your agent to solve increasingly complex problems.
The path forward involves chaining these tools together, allowing the agent to perform multi-step planning. But for now, you have successfully moved from an AI user to an AI architect. The next phase of your development journey—building multi-step, multi-tool agents—awaits.

 Nana Wu
 Asro

 Laily UPN

 Iffa Jayyana

 Rifan Muazin

 Suro Senen

 Lina Hope

