
 Ali Ikhwan
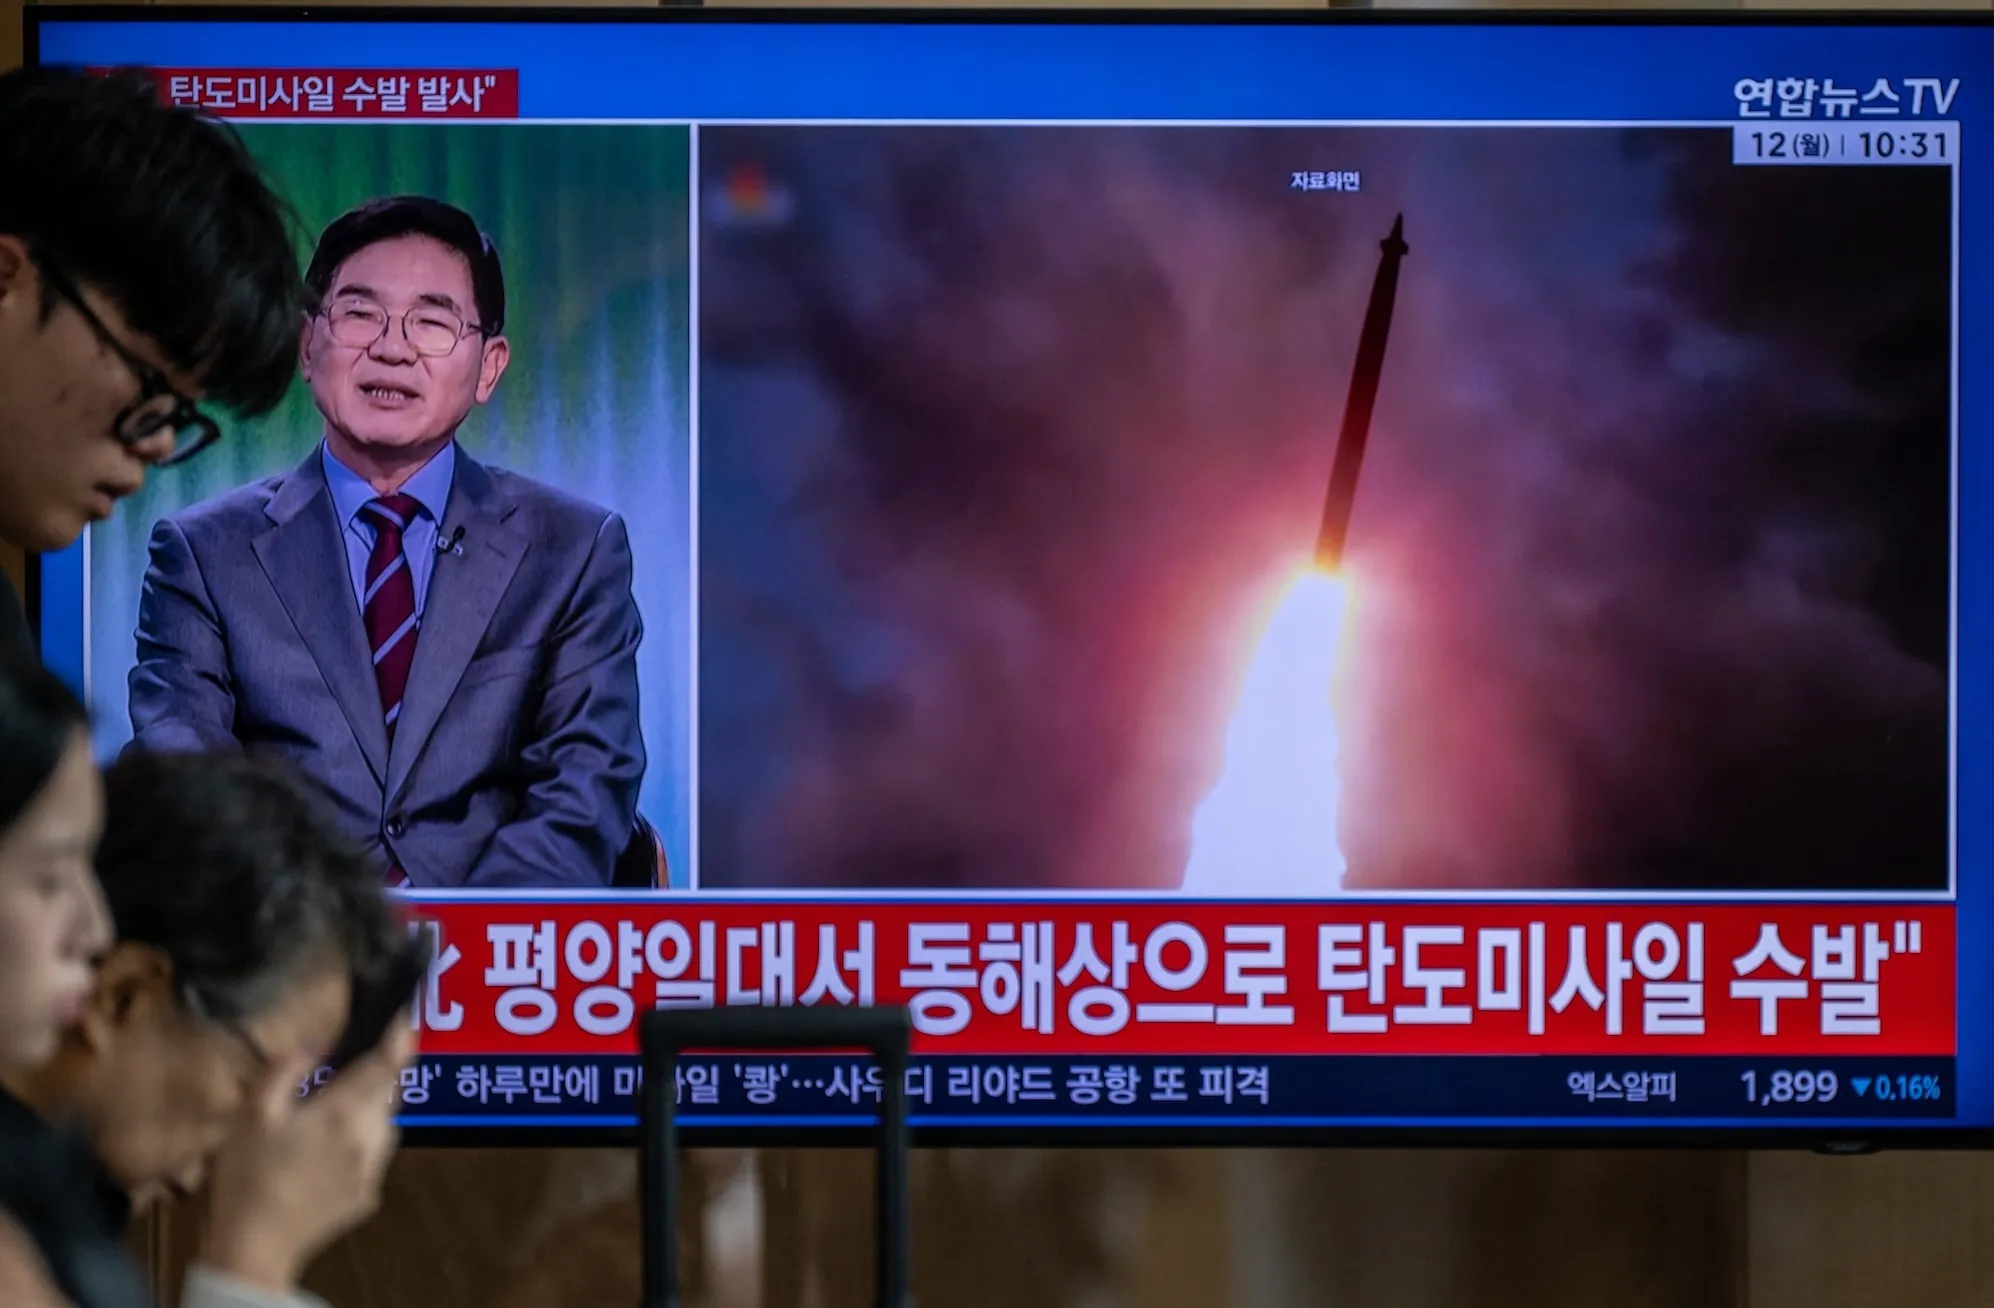
In a sprawling national security operation that exposes the sophisticated lengths to which the North Korean regime will go to bypass international sanctions, the U.S. Department of Justice (DOJ) has unveiled a massive crackdown on "laptop farms" operated by American facilitators. These domestic hubs served as the digital infrastructure for North Korean state-sponsored IT workers to embed themselves within U.S. companies, siphoning data and capital to fuel Pyongyang’s nuclear ambitions.
The operation, which involved the execution of dozens of search warrants across Texas and the seizure of over 180 computers, represents a significant escalation in the ongoing cat-and-mouse game between Western intelligence agencies and the Kim Jong Un regime’s clandestine cyber units.
The Mechanics of the "Laptop Farm" Scheme
The strategy employed by North Korean operatives is as audacious as it is simple: they assume the identities of U.S. citizens to secure legitimate remote-work contracts. By posing as American IT professionals, they gain access to company internal networks, sensitive intellectual property, and payroll systems.
However, because these hackers are physically located in North Korea or neighboring regions, they face a significant logistical hurdle: their IP addresses and digital footprints would immediately flag them to corporate security systems. To circumvent this, the regime recruits or coerces U.S.-based "facilitators."
The Role of the Facilitator
These American facilitators operate "laptop farms"—physical locations, often residential, where they maintain dozens of laptops shipped by unsuspecting U.S. employers. When a victim company hires a "remote employee," they send a company-issued laptop to an address provided by the applicant. That address is actually a laptop farm.
Once the device is plugged in, the North Korean operator logs in remotely from overseas, using the U.S.-based machine as a proxy. To the victim company, the traffic appears to originate from a domestic residence or home office, effectively bypassing geographic security blocks. The DOJ reports that these facilitators not only manage the hardware but also provide the necessary local credentials to maintain the illusion of a domestic employee.
Chronology of the Infiltration
The evolution of this threat has been documented over the past several years, shifting from sporadic attacks to a highly industrialized, state-backed enterprise.
- 2023-2024 (The Expansion Phase): North Korean hackers began aggressively targeting Western tech firms, leveraging sophisticated social engineering on platforms like LinkedIn. Using spoofed profiles and synthetic identities, they secured roles in sectors ranging from healthcare to communications.
- Early 2025: Cybersecurity firms, including CrowdStrike, noted a surge in "hands-on-keyboard" intrusions. Unlike automated malware attacks, these involved human operators actively navigating networks, mimicking the behavior of legitimate employees to avoid detection.
- Late 2025: The scale of the illicit revenue became clear, with reports suggesting North Korean hackers were behind nearly half of all documented intrusions in the U.S. tech sector.
- Tuesday (The DOJ Announcement): Federal authorities confirmed the indictment and arrest of at least two U.S.-based facilitators. The operation resulted in the raid of over 40 distinct residential locations across Texas, marking the largest enforcement action of its kind in history.
Supporting Data: A Multi-Billion Dollar Threat
The scale of the financial impact is staggering. According to the DOJ, at least 70 U.S.-based companies have been compromised by these remote workers. While the immediate loss identified in this specific bust is roughly $3 million, experts believe this is merely the tip of the iceberg.
The Financial Pipeline
The regime’s cyber-operations are intrinsically linked to its survival. By embedding workers in U.S. firms, Pyongyang achieves three goals:
- Direct Salary Theft: These workers collect legitimate paychecks, which are funneled back to the regime.
- Intellectual Property Theft: By gaining access to corporate source code and proprietary research, hackers extort the companies for further payments.
- Capital Diversion: Beyond the "remote worker" scheme, the regime continues to pillage crypto exchanges and open-source projects. In 2025 alone, the regime was linked to the theft of at least $2 billion in cryptocurrency.
The combination of these revenue streams provides the necessary liquidity to maintain the regime’s nuclear and ballistic missile programs, which are currently under heavy international sanctions.
Official Responses and Strategic Disruption
The DOJ’s recent action was the result of a coordinated effort involving the FBI and private-sector security giants. CrowdStrike, which provided technical assistance to the FBI, emphasized the "vital" nature of these laptop farms to the North Korean strategy.
"Laptop farms are essential to their operation," a CrowdStrike spokesperson noted. "They overcome the physical, financial, and legal challenges of not being present in the target country. By subcontracting the hardware management to domestic facilitators, they minimize their own exposure while maximizing their footprint within the target network."
The FBI’s Warning
In a separate public service announcement, the FBI highlighted that there are likely "thousands" of these state-controlled workers currently active in Western companies. The Bureau warned that this constitutes a "significant national security and intellectual property theft insider threat," noting that once these workers are inside a network, they are often indistinguishable from regular employees until a breach occurs.
Implications: A New Era of Insider Threats
The shift toward utilizing domestic facilitators creates a paradigm shift in how corporate America must defend itself. Traditional cybersecurity—firewalls, endpoint protection, and VPNs—is often insufficient when the "hacker" is a human being with valid, albeit stolen, credentials.
The Erosion of Trust
The "remote work" model, which surged in popularity following the COVID-19 pandemic, has inadvertently provided the perfect cover for state-sponsored espionage. Companies are now faced with a difficult dilemma: tighten remote hiring practices, potentially slowing recruitment and increasing costs, or accept a higher risk profile.
The "Extortion" Loop
The DOJ highlighted a disturbing trend where, after successfully infiltrating a company, the hackers transition from "employees" to "extortionists." They threaten to release sensitive customer data or destroy intellectual property unless the company pays a ransom. This creates a cycle of victimization where the companies are initially paying salaries to their own attackers, only to be hit with further demands once the attackers have sufficient leverage.
Beyond Tech
While the tech industry has been the primary target, the reach of these operations is broad. Healthcare, manufacturing, retail, and communications sectors across 16 states and the District of Columbia have all been hit. This indicates that the North Korean intelligence services are not just looking for "hacks," but for systemic access to the vital sectors that keep the American economy running.
Conclusion: The Path Forward
The crackdown in Texas is a tactical victory, but the strategic challenge remains. As long as the North Korean regime views the internet as a primary battlefield for generating revenue and state secrets, U.S. companies will remain in the crosshairs.
The FBI and DOJ are urging companies to implement stricter identity verification protocols for remote hires, including rigorous video-based background checks and a closer monitoring of hardware shipping addresses. However, as the regime adapts—likely by moving toward more decentralized or "work-from-home" facilitation models—the defense must also evolve.
The message from federal authorities is clear: the threat is no longer coming from a distant server rack in Pyongyang. It is coming from a quiet residential street in Texas, through a company-issued laptop, by an employee who never existed. For American businesses, the era of absolute trust in remote hiring is over; in its place, a new, more skeptical era of digital verification has begun.

 Neng Nana
 Siti Muinah
 Nana Wu
 Asro
 Jia Lissa
 Dwi Wanna
