
 Muslim
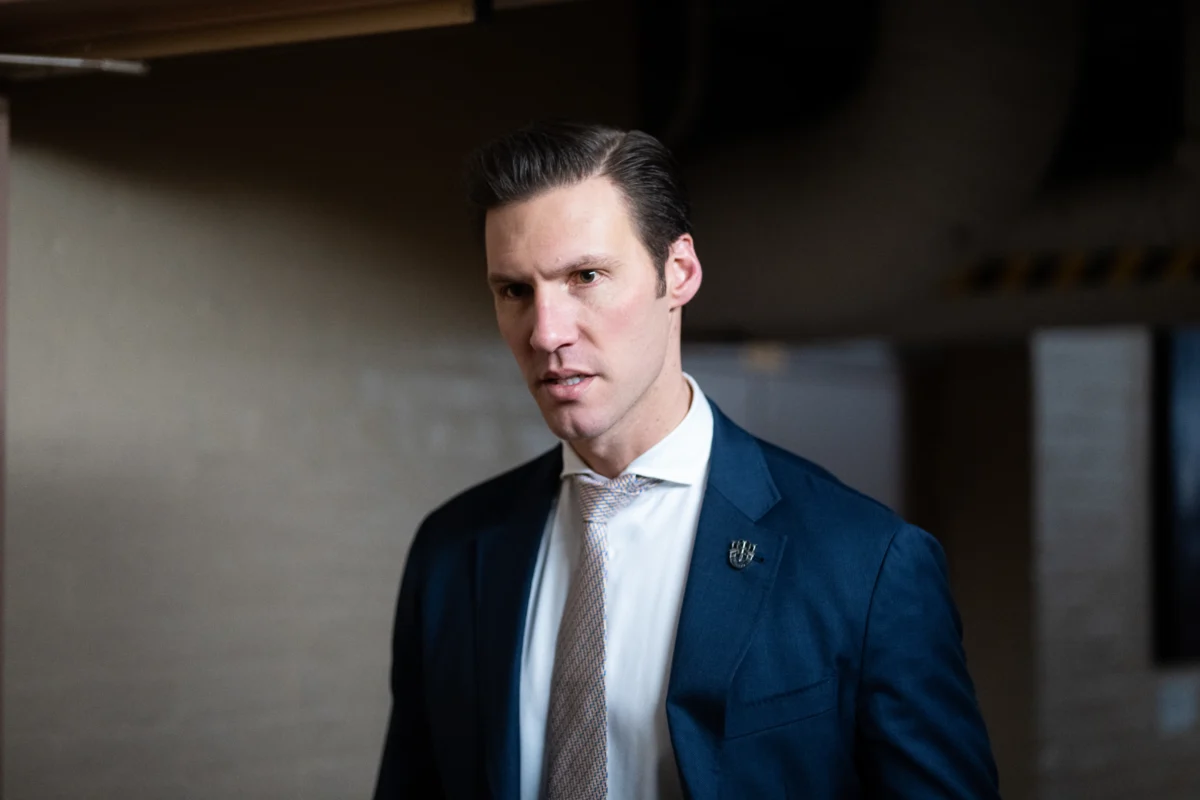
In a significant legislative move aimed at securing America’s technological edge, a bipartisan duo in the U.S. House of Representatives has introduced the AI Cyber Defense Act. The bill, spearheaded by Reps. Pat Harrigan (R-N.C.) and George Whitesides (D-Calif.), seeks to task the National Institute of Standards and Technology (NIST) with the critical mission of establishing formal, voluntary guidelines to shield domestic artificial intelligence models from "distillation attacks."
As the global AI arms race intensifies, this legislation represents one of the first formal attempts to address the economic and national security threats posed by foreign adversaries who allegedly bypass the heavy lifting of R&D by siphoning the capabilities of U.S.-developed frontier models.
The Core Challenge: What is a Distillation Attack?
At its simplest, a distillation attack occurs when an entity uses a smaller, less capable AI model to "learn" from the outputs of a larger, more powerful frontier model. By feeding millions of prompts into a sophisticated system like those developed by OpenAI, Anthropic, or Google, an adversary can capture the logic, reasoning patterns, and latent capabilities of the original model.
This process effectively allows foreign actors to "piggyback" on the hundreds of millions of dollars invested in U.S. research. The result is a cheaper, faster path to parity, allowing competitors to achieve high-performance results without the commensurate expenditure in hardware, data curation, or human talent.
The Strategic "Free-Rider" Problem
Rep. Pat Harrigan, in an exclusive interview with CyberScoop, framed the issue as an existential threat to American innovation. He argues that U.S. AI companies are currently burning through capital to maintain a six-to-12-month lead in the sector.
"One of my concerns is that our adversaries just see it as much more beneficial and productive for them as this U.S. industry engine burns," Harrigan noted. "They hang six to 12 months behind the United States, let us burn really hot, and for 5 to 10% of the spend, they can just distill and steal. They can do that until the point where our market kind of falters, at which point they can turn it into high gear and leapfrog us."
Chronology of Escalation: From Research to Malicious Campaigns
The concern over model theft is not purely theoretical. Over the past 24 months, the landscape of AI security has shifted from abstract fears to documented, systematic campaigns.
- 2023–2024: Major AI labs begin reporting suspicious, high-volume traffic patterns originating from proxy networks. Security teams at Anthropic and OpenAI identify that these aren’t typical user queries, but rather structured, iterative attempts to "decompile" the models’ reasoning.
- Late 2024: The U.S. government, alongside industry titans like Google and OpenAI, begins publicly signaling that companies such as China’s Moonshot AI, DeepSeek, and Alibaba have been involved in systematic efforts to scrape U.S. model outputs.
- December 2025: High-level policy discussions in Washington culminate in the drafting of the AI Cyber Defense Act, as lawmakers recognize that voluntary company measures are insufficient against state-sponsored or state-backed corporate espionage.
- October 2026: The AI Cyber Defense Act is formally introduced, seeking to codify NIST’s role in defining and defending against these techniques.
Supporting Data: The Mechanics of Theft
The scale of these operations is staggering. According to cybersecurity experts monitoring the situation, these campaigns utilize sophisticated infrastructure to bypass standard geographic and security blocks.
- Burner Account Networks: Adversaries employ thousands of resold or burner accounts to distribute queries across a wide range of IP addresses, making it difficult for automated systems to detect an individual malicious actor.
- Prompt Engineering at Scale: Rather than simple questions, attackers use millions of complex, adversarial prompts designed to elicit "chain-of-thought" reasoning from the target model.
- Data Exfiltration: The captured outputs are then used as training data for domestic models in foreign jurisdictions—specifically targeting Russia, China, Iran, and North Korea.
NIST faces a complex initial task: they must legally define a "distillation attack" in a way that captures these malicious campaigns without chilling the legitimate, collaborative ecosystem of open-source and open-weight AI, which is itself a massive driver of global innovation.
Official Responses and Political Implications
The legislation has garnered support from both sides of the aisle, reflecting a rare consensus on the necessity of protecting American intellectual property.
Rep. George Whitesides (D-Calif.)
"AI is advancing at a breakneck pace," Rep. Whitesides said in a statement. "Every month we keep China and other adversaries from stealing our progress is a month we gain to build the safeguards this technology needs."
The NIST Mandate
The bill proposes the creation of an "AI Cybersecurity Roundtable" within NIST. This body would serve as a forum for frontier AI companies, hardware manufacturers, and security experts to synthesize a set of "off-the-shelf" defensive standards.
Harrigan emphasized that this is about creating a baseline of preparedness. "I envision a place where you can go and pick an off-the-shelf set of standards that says these are the best practices as we know them today, given the current state of technology and the threats that are out there."
The "Entities of Concern" Framework
A crucial component of the bill is its definition of "entities of concern." It specifically targets organizations headquartered in Russia, China, Iran, and North Korea, or those operating under the direction of entities based in those nations. The Director of NIST is granted the authority to update this list, providing the government with the agility needed to respond to an evolving threat landscape.
Broader Implications: The AI Industry’s Dilemma
While the bill focuses on foreign threats, the industry is simultaneously navigating internal pressure. U.S. AI firms are currently embroiled in multiple class-action lawsuits filed by authors, artists, and media organizations. These plaintiffs allege that the very models the government is now trying to "protect" were built using copyrighted works without authorization.
This creates a complex narrative for the industry: they are simultaneously fighting to prevent the theft of their own "innovation" while defending themselves against accusations of "theft" regarding their training data.
The Path Forward
If the AI Cyber Defense Act passes, it will mark a pivotal shift in how the U.S. treats AI models—not just as software products, but as critical national infrastructure.
Key Objectives of the Act:
- Standardization: Establishing uniform best practices for AI security.
- Deterrence: Creating clear legal definitions that categorize model distillation as a prohibited activity by foreign entities of concern.
- Collaboration: Bridging the gap between the private sector’s speed and the federal government’s regulatory stability.
As the bill moves toward committee, the technology sector will be watching closely. While voluntary standards are generally welcomed, the challenge remains to ensure that these regulations provide genuine security without imposing a burden that stifles the very "engine of innovation" that Washington is so keen to protect.
The future of AI dominance, according to this legislation, will not be won simply by being the fastest to build, but by being the most resilient in protecting what has already been built. The coming months will determine if this bipartisan effort can successfully navigate the fine line between defensive security and the preservation of an open, competitive global AI market.

 Siti Muinah
 Raul Delapena Setiawan

 Ammar Sabilarrohman

 Asep Darmawan

 Asro

 Layla Zulfa

 Nila Kartika Wati

