
 Raul Delapena Setiawan
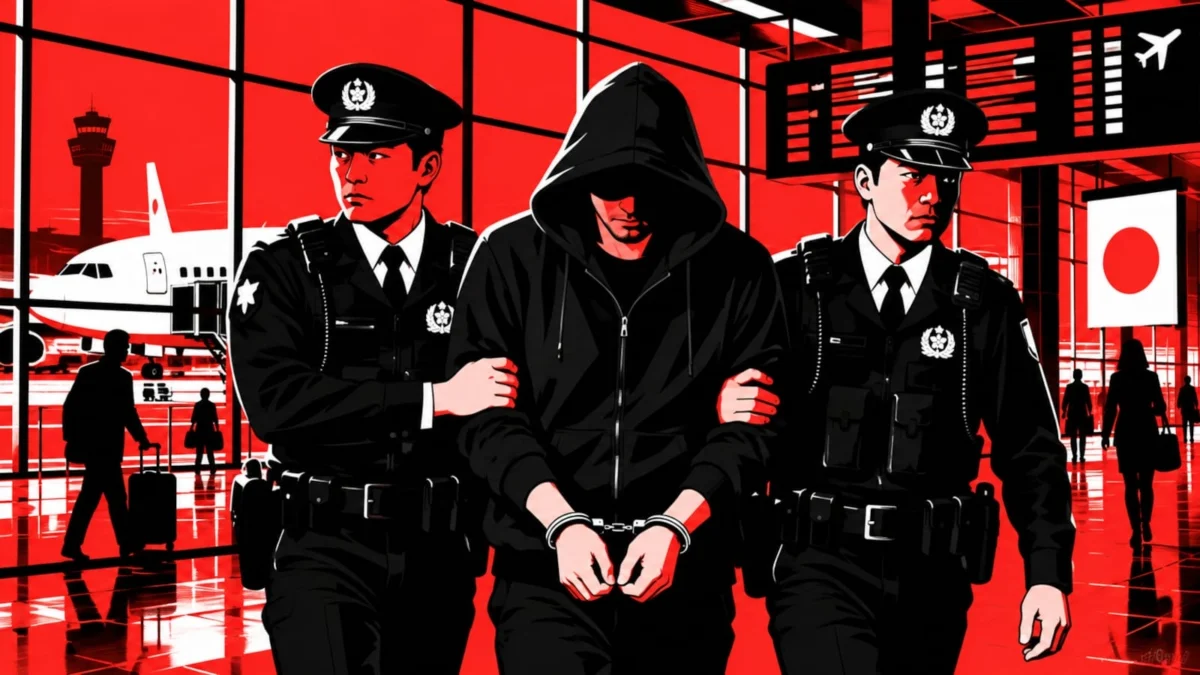
In a significant victory for international law enforcement, a Russian national identified as a high-ranking member of the notorious Qilin ransomware syndicate has been extradited to Germany. The arrest and subsequent transfer represent a pivotal moment in the ongoing global effort to dismantle the infrastructure of "Ransomware-as-a-Service" (RaaS) operations that have plagued multinational corporations, government agencies, and critical infrastructure providers for years.
The extradition, confirmed by Japan’s National Police Agency (NPA) this week, concludes a months-long legal process that began when the suspect was apprehended in Osaka while traveling as a tourist. The operation underscores the efficacy of cross-border intelligence sharing and the increasing vulnerability of cybercriminals who rely on international travel to conduct their affairs.
The Arrest: A Coordinated International Effort
The apprehension of the alleged Qilin operative was not a matter of chance, but the result of a meticulously coordinated operation between German federal authorities and their Japanese counterparts. According to official statements released by the Japanese National Police Agency, the suspect had been the subject of a German-issued international arrest warrant related to a devastating ransomware incident on German soil.
The Timeline of Capture
- May 2026: The suspect is identified and detained by Japanese authorities at a hotel in Osaka. The arrest was executed following the receipt of a provisional detention warrant.
- June – September 2026: Legal proceedings take place within the Japanese judicial system to satisfy the requirements of the Extradition Law for Fugitives. This period involved complex collaboration between the Japanese Ministry of Justice, the Tokyo High Public Prosecutors Office, and German federal investigators.
- October 2026: Following the approval of the extradition request, the suspect is officially transferred to German custody to face prosecution.
"When a Russian national for whom Germany had obtained an arrest warrant… arrived in Japan, the Japanese Ministry of Justice, the Tokyo High Public Prosecutors Office, and Germany worked together to detain the suspect… and then facilitated the extradition," the NPA stated in its official press release.
Anatomy of a Threat: The Qilin Ransomware Group
Qilin, also known in its early stages as "Agenda," emerged on the threat landscape in August 2022. It quickly established itself as a premier RaaS operation, offering its encryption tools and infrastructure to affiliates in exchange for a percentage of the extortion proceeds.
Double-Extortion Tactics
The group’s methodology is rooted in the "double-extortion" model. Rather than merely encrypting files to hold them hostage, Qilin operatives exfiltrate sensitive data before triggering the encryption process. This dual pressure—threatening both the loss of system access and the public leak of proprietary or sensitive user data—compels victims to pay ransoms, often in the millions of dollars.
Global Reach and Impact
Since its inception, Qilin has transformed into one of the most prolific threats in the digital ecosystem. Recent forensic analysis suggests the group has successfully targeted more than 2,350 unique organizations spanning 62 countries. Their victimology is diverse, spanning industries from manufacturing and logistics to public sector legal services and government agencies.
Notable victims include:
- Nissan: The Japanese automotive giant suffered a significant breach of its design studio data.
- Asahi Group: The largest beer producer in Japan faced a crippling attack that forced a prolonged suspension of operations and exposed the personal information of 1.5 million customers.
- Lee Enterprises: The U.S.-based media conglomerate saw its data leaked following a failure to meet the group’s ransom demands.
- Court Services Victoria: An Australian judicial body that had court recordings and sensitive data exposed in an attack.
Technical Sophistication and Zero-Day Exploitation
Qilin’s rise to prominence is not merely a result of aggressive extortion but also of technical sophistication. The group has demonstrated an uncanny ability to pivot quickly to exploit vulnerabilities in remote access infrastructure.
Exploiting the VPN Perimeter
A hallmark of Qilin’s recent campaigns has been the weaponization of critical vulnerabilities in Virtual Private Network (VPN) appliances. Security researchers at Check Point have linked the group to the exploitation of zero-day vulnerabilities in common VPN hardware, while other instances have seen the group leveraging known "n-day" flaws in Palo Alto Networks’ GlobalProtect.
By gaining initial access through these perimeter devices, the group is able to move laterally across enterprise networks, escalate privileges, and establish persistence long before the victim realizes they have been breached.
The ATF Incident
Perhaps the most high-profile evidence of their reach was the recent breach of the U.S. Bureau of Alcohol, Tobacco, Firearms and Explosives (ATF). The incident served as a stark reminder that even the most secure government agencies are not immune to the sophisticated reconnaissance and infiltration techniques employed by RaaS operators.
Implications for the Ransomware Landscape
The arrest of a core member of the Qilin organization is a significant blow to the group’s operational continuity, but industry experts caution that it does not spell the end of the threat.
The Resilience of RaaS
The RaaS model is designed for resilience. Because the "core" team provides the infrastructure and the "affiliates" conduct the actual attacks, the arrest of a key administrator or developer may disrupt operations temporarily, but it rarely collapses the entire network. Since the suspect was initially detained in May, Qilin has continued to operate, listing more than 450 new victims on its data leak site since June alone.
Legal Precedent and Deterrence
However, this case sets a vital legal precedent. By successfully navigating the complexities of international extradition for a cybercrime suspect, Germany and Japan have signaled that the "safe haven" status often enjoyed by Russian-based cybercriminals is shrinking. The move effectively limits the global mobility of key players within these criminal syndicates, making it riskier for them to travel or interact with the global financial system.
Strengthening the Security Blueprint: Lessons for Defenders
As the threat landscape evolves, organizations must shift their defensive strategies to account for the speed and precision of groups like Qilin. The era of simple perimeter defense is over; today’s defenders must adopt a "validate and fix" mindset.
Preparing for AI-Powered Attacks
With the integration of artificial intelligence into cyber-offensive playbooks, the time between initial exploitation and full network encryption is shrinking. Organizations are encouraged to:
- Prioritize Patch Management: As evidenced by the group’s use of VPN zero-days, rapid patching of edge-facing appliances is non-negotiable.
- Zero Trust Architecture: Implement strict segmentation to prevent lateral movement if a perimeter breach occurs.
- Threat Intelligence: Leverage real-time intelligence feeds to identify indicators of compromise (IoCs) associated with known ransomware affiliates.
As industry leaders like Mikko Hyppönen and security experts from global firms continue to advocate, the focus must shift from reactive patching to proactive validation. Defenders must be able to test their environments against simulated attacks, identify gaps at machine speed, and remediate them before a threat actor like Qilin can leverage a vulnerability.
A New Chapter in International Cooperation
The extradition of the Qilin operative serves as a beacon of hope for a more collaborative international approach to cyber-policing. While the ransomware threat remains persistent, the ability of sovereign nations to cooperate across judicial lines creates a tangible cost for those who profit from global digital disruption. As the investigation into the Qilin group continues, the global security community remains vigilant, awaiting the next development in what has become a high-stakes, real-world battle against digital extortionists.

 Nana Muazin
 Ali Ikhwan

 Dwi Wanna

 Muslim

 Nana Wu


 Rifan Muazin
 Asro
