
 Muslim
The European retail sector is grappling with a series of high-profile cybersecurity incidents that have triggered operational paralysis, raised consumer privacy concerns, and highlighted the fragility of interconnected digital supply chains. In a span of less than a week, multiple retail giants—ranging from multinational supermarket conglomerates to high-street fashion houses—have been forced to take drastic measures to mitigate unauthorized intrusions into their IT environments.
These events, occurring in rapid succession, have sent shockwaves through the industry, prompting a scramble to bolster defenses and sparking an urgent debate regarding the resilience of modern retail infrastructure. While there is currently no evidence linking these disparate attacks, the frequency and timing of the breaches have placed the entire sector on high alert.
The Chronology of Disruption
The current wave of instability began in mid-October, manifesting across different geographies and business models.
October 11–12: The Initial Breach
The cascade of incidents arguably began with a sophisticated, albeit distinct, attack in France. Numerous supermarket chains reported a malicious intrusion targeting their operational technology (OT) rather than their traditional IT networks. Attackers successfully breached the refrigeration control systems of multiple retailers overnight. By manipulating the temperature sensors and climate management software, the perpetrators forced a mass spoilage of food inventory, resulting in financial losses estimated in the hundreds of thousands of euros.
Simultaneously, on October 11, the South African retail powerhouse The Foschini Group (TFG) discovered a security breach affecting its UK subsidiary, TFG London. By the following day, the situation had escalated, forcing the company to initiate an investigation into the impact on its IT systems.
October 12: Ahold Delhaize Takes Systems Offline
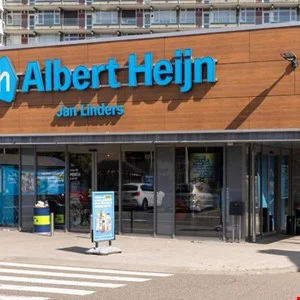
On October 12, the Netherlands-based multinational Ahold Delhaize issued a formal notice confirming a "security issue" within its internal networks. As a precautionary measure, the group opted to take several key systems offline to contain the threat and prevent lateral movement within its architecture. The disruption hit three of its prominent brands: the supermarket chain Albert Heijn—a staple in the Netherlands and Belgium—along with the Dutch drugstore chain Etos and the liquor retailer Gall & Gall.
October 13: ASOS and H&M Under Scrutiny
By October 13, the crisis expanded further. Customers of the UK-based online fashion retailer ASOS received alarming, unauthorized push notifications suggesting that the company had been hacked. Simultaneously, media reports indicated that the retail giant H&M was investigating claims of a potential data compromise circulating online, although the company maintained that no evidence of an internal breach had been found at that time.
A Deep Dive into the Impacted Organizations
The sheer variety of the targeted entities—from physical grocery chains to digital-first fashion retailers—demonstrates that no corner of the retail ecosystem is immune.
The Ahold Delhaize Response
Ahold Delhaize’s decision to take systems offline represents a textbook "fail-safe" approach to cybersecurity. By severing network connectivity, the organization prioritized the integrity of its data over immediate operational uptime. However, for a multinational with such a deep footprint in the Benelux region, the impact was significant, affecting everything from inventory management to point-of-sale functionality at the store level.
The Foschini Group (TFG) and Operational Segmentation
TFG’s incident provides a crucial case study in the importance of network segmentation. While TFG London was compromised, the company confirmed that its other high-street brands, such as Inside Story and White Stuff, remained unaffected. Furthermore, the firm’s subsidiaries in Africa and Australia continued to operate without interruption.
Industry experts have lauded this structure. Muhammad Yahya Patel, vCISO and cybersecurity advisor for EMEA at Huntress, noted: "The fact that Inside Story and White Stuff within the same group were unaffected, and that TFG’s wider Africa and Australia operations were untouched, suggests some degree of system separation was in place. That separation, which limited the blast radius, is worth noting as a positive."
The ASOS Notification Incident
The ASOS incident serves as a reminder that cybersecurity is as much about communication as it is about firewalls. The company confirmed an unauthorized intrusion into the third-party platforms it utilizes for customer engagement. While personal information, such as names and contact details, was accessed, the company moved quickly to assure customers that payment-card data and passwords remained encrypted and untouched. The unauthorized push notification, however, caused significant public panic, underscoring how attackers can weaponize a company’s own communication channels to cause reputational damage.
Supporting Data and Technical Implications
To understand the severity of these events, one must look at the technical architecture of modern retail. Most modern retailers operate on "hybrid" models, where legacy POS systems are connected to cloud-based inventory management tools, which in turn are integrated with third-party marketing and customer relationship management (CRM) platforms.
The Vulnerability of Third-Party Integrations
The ASOS incident highlights a growing trend: the exploitation of third-party vendors. As retailers outsource marketing automation and communication tools to specialized vendors, they expand their "attack surface." If a vendor’s API is compromised, attackers can gain a backdoor into the retailer’s ecosystem, even if the retailer’s internal core systems are well-defended.
Operational Technology (OT) as a Target
The French supermarket attack represents a shift from data theft to physical sabotage. By targeting refrigeration systems, the attackers moved beyond the "digital" realm to cause direct, tangible financial damage. This indicates that attackers are increasingly looking for "soft" targets in the physical infrastructure—systems that may not be monitored with the same rigor as an e-commerce database.
Official Responses and Remediation Efforts
The response from the retail sector has been one of transparency—or at least, the attempt at it.
- Regulatory Reporting: TFG has already confirmed that it has reported its breach to the relevant UK authorities. Such moves are not only legally required under frameworks like the GDPR but are also essential for coordinating intelligence with national cybersecurity centers.
- Public Reassurance: Retailers like ASOS and TFG have been quick to explicitly state that payment information was not at risk. In the retail sector, trust is the primary currency. By proactively confirming that banking details remain secure, these companies are attempting to stem the tide of potential customer churn.
- Cautious Investigation: Companies like H&M have demonstrated the necessity of a calm, evidence-based approach. By publicly verifying that there is no indication of a compromise, they prevent the spread of misinformation that could lead to unnecessary panic among shareholders and consumers alike.
Strategic Implications: Lessons for the Future
The wave of incidents across Europe serves as a wake-up call for the retail industry. As we look toward the future, several strategic shifts appear inevitable.
The Shift Toward "Zero Trust" Architecture
The "blast radius" observed in the TFG incident proves that network segmentation is no longer a "nice-to-have" feature; it is a fundamental requirement. Retailers will likely accelerate the adoption of Zero Trust architectures, which assume that a breach is inevitable and focus on preventing an intruder from moving laterally from one system to another.
Enhanced Vendor Risk Management
The ASOS breach will undoubtedly lead to tighter scrutiny of third-party platforms. Retailers will be forced to demand higher levels of transparency and security certification from their marketing, logistics, and IT service providers. The cost of a breach at a minor vendor is now too high for a major retailer to ignore.
Investing in OT Security
The attack on French supermarkets serves as a grim warning regarding the vulnerability of the "Internet of Things" (IoT) and OT. Retailers must begin treating their refrigeration, HVAC, and building management systems as high-priority security assets, rather than simple utility infrastructure.
The Role of Transparency in Crisis Management
Finally, these incidents underscore the importance of clear, timely communication. In an age of social media, the speed at which a breach becomes "public knowledge" is faster than ever. Companies that control the narrative—by confirming what is and isn’t affected early on—stand a much better chance of retaining customer trust.
Conclusion
The European retail sector is currently navigating a period of unprecedented digital turbulence. While the individual incidents may appear isolated, they reflect a broader reality: as retailers become more efficient through digital integration, they also become more vulnerable. The lessons learned from this month’s disruptions—namely the power of network segmentation, the necessity of securing third-party integrations, and the importance of protecting physical operational technology—will define the cybersecurity strategy of the retail sector for years to come.
For now, the industry remains in a state of high vigilance. As authorities continue their investigations into these incidents, retailers are left with a clear directive: the digital transformation of the high street must be matched by a transformation in how that digital landscape is protected. The survival of the retail brand in the 21st century depends as much on its ability to stop a hacker as it does on its ability to stock a shelf.

 Ali Ikhwan
 Raul Delapena Setiawan
 Nana
 Asep Darmawan
 Neng Nana
