
 Laily UPN
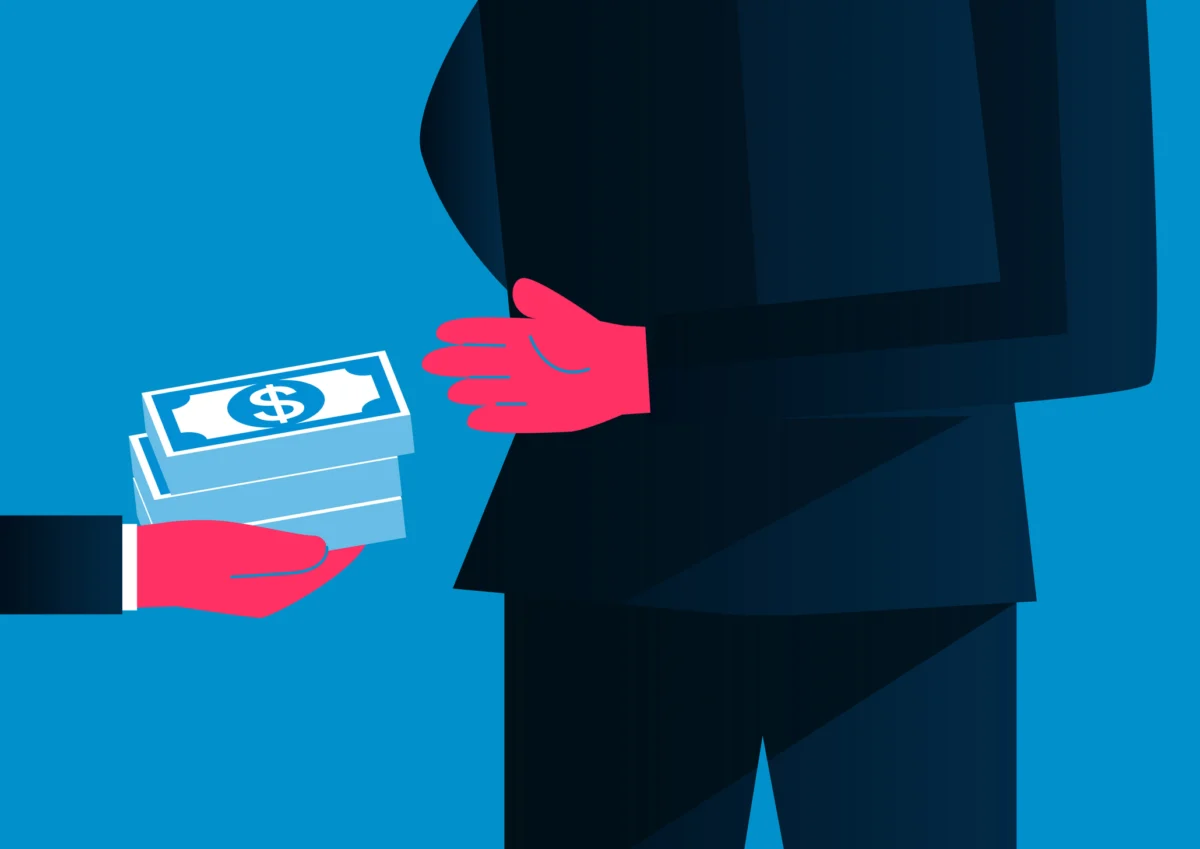
In a startling case that exposes the dark underbelly of the cybersecurity remediation industry, federal authorities have charged Zohar Pinhasi, the owner of Florida-based MonsterCloud, with running an elaborate, multi-year fraud scheme. Prosecutors allege that Pinhasi exploited companies already reeling from ransomware attacks, masquerading as a high-tech savior while secretly funneling client funds to the very cybercriminals who had crippled their operations.
The indictment, unsealed in a Brooklyn federal court, paints a picture of a calculated deception in which Pinhasi charged desperate clients exorbitant fees for "proprietary" decryption services that did not exist. Instead, Pinhasi allegedly acted as an undisclosed middleman, pocketing massive markups while paying off hackers to obtain the decryption keys he claimed to have engineered himself.
The Mechanics of the Fraud
The scheme, which operated over a five-year period concluding in 2023, allegedly targeted hundreds of businesses across the United States and Canada. Pinhasi and his associates at MonsterCloud reportedly positioned themselves as a premium alternative to paying ransoms, promising clients that they possessed specialized, proprietary tools to recover encrypted data without engaging with criminal extortionists.
According to the Justice Department, the operation followed a deceptive playbook:
- The Hook: MonsterCloud would solicit an initial "exploratory fee" from victimized companies, typically ranging between $2,500 and $10,000.
- The False Proof: After obtaining a ransom note and a sample of encrypted files from the client, Pinhasi would secretly contact the cybercriminals. He would secure a decryption tool from them and then present it to the client as proof of his own proprietary technological prowess.
- The Upsell: Having "proven" his capabilities, Pinhasi would induce the client to sign a contract for full-scale recovery, often charging fees that were two to three times the cost of the actual ransom demand.
- The Secret Payout: Behind the scenes, Pinhasi would pay the hackers the actual ransom amount while leading the client to believe that the decryption was achieved through MonsterCloud’s exclusive, in-house technical wizardry.
Chronology of Deception
The allegations against Pinhasi are not entirely new to the cybersecurity community. As far back as 2019, investigative reporting by ProPublica cast a spotlight on MonsterCloud, detailing how the company was effectively operating as a front for ransom payments. Despite the scrutiny and public questions regarding his business model, Pinhasi continued to operate MonsterCloud, allegedly refining his methods to extract maximum profit from victims.
- Pre-2019: MonsterCloud begins establishing its footprint in the ransomware response market, branding itself as a "remediation" firm.
- 2019: Reports emerge questioning the company’s "proprietary" recovery methods. Despite these warnings, the firm continues to land contracts with various organizations, including, allegedly, law enforcement agencies.
- 2018–2023: The period cited in the federal indictment during which Pinhasi and his co-conspirators allegedly defrauded clients of more than $19 million.
- August 2023: A specific instance noted in the indictment where Pinhasi charged a client roughly $150,000 for recovery services, while the actual ransom paid to the hackers was a mere $8,200.
- October 2026: Federal authorities officially charge Pinhasi with two counts of wire fraud and one count of wire fraud conspiracy.
- Present Day: Pinhasi, a dual U.S.-Israeli national, has pleaded not guilty. He was released on a $2 million bond, with legal teams currently engaged in plea negotiations.
Supporting Data: The Cost of Betrayal
The financial scale of the operation is staggering. Over the five-year window identified by federal investigators, Pinhasi is accused of orchestrating a scheme that moved over $8 million into the hands of cybercriminals. By keeping his clients in the dark, he not only defrauded them of the price difference between his fees and the ransom but also prevented them from making informed decisions regarding their own data security and incident response strategy.
The indictment highlights the use of aliases, such as "Zack Silver" and "Zack Green," which Pinhasi purportedly used when communicating with the ransomware gangs. These monikers were essential to maintaining the illusion that he was a third-party expert rather than a direct conduit for criminal payments.
Official Responses and Legal Implications
The Department of Justice has been unequivocal in its condemnation of the scheme. "By falsely claiming to decrypt ransomware without paying off the ransomers, the defendant re-victimized his clients while extracting a hefty profit for himself," said Joseph Nocella Jr., U.S. attorney for the Eastern District of New York.
The FBI has also weighed in, highlighting the damage done to the trust necessary for effective cybersecurity response. "Pinhasi claimed to fix ransomware while never remediating the underlying threat. Instead, he turned the victim’s crisis into his own profit center," noted James C. Barnacle Jr., assistant director of the FBI. "This deception is unacceptable."
If convicted on all charges, Pinhasi faces up to 60 years in federal prison. The case has been marked by a one-month delay in trial proceedings as defense and prosecution attorneys attempt to negotiate a potential plea, a move that suggests the weight of the evidence against the former CEO may be substantial.
The Broader Implications for Cybersecurity
The Pinhasi case serves as a grim case study in how the "shadow economy" of ransomware response can be weaponized against the very victims it purports to serve. When asked about the vulnerability of companies to such scams, Jon DiMaggio, principal researcher at Arkem Cyber, expressed frustration: "It baffles me that companies fall for this. I mean, they just got hacked and they go straight to a shady source."
The reality is that companies in crisis are often desperate for a quick resolution. This desperation creates a vacuum where "remediation" firms can thrive. The MonsterCloud case is not an isolated incident; earlier this year, three former ransomware negotiators were sentenced to prison for a similar scheme involving the exploitation of their own clients.
Key Lessons for Organizations
The exposure of MonsterCloud’s operations provides a critical checklist for organizations navigating a potential ransomware event:
- Vetting is Mandatory: Companies must perform rigorous due diligence on any third-party cybersecurity firm. If a firm claims to have "secret" or "proprietary" decryption tools that no one else in the industry has heard of, it is a significant red flag.
- Transparency is Non-Negotiable: Legitimate remediation firms should be transparent about their methods. If they are negotiating with hackers, they should be upfront about the risks, the legal implications, and the total cost.
- Avoid "The Quick Fix" Mindset: The desire for a rapid return to business as usual is exactly what criminals and predatory "consultants" rely on. Organizations should prioritize engagement with established, reputable incident response firms that work in tandem with law enforcement and insurance providers.
- Continuous Monitoring: As seen in the MonsterCloud case, these companies often keep their websites active, complete with forged testimonials and credentials. Organizations should rely on peer reviews and industry certifications rather than testimonials found on a firm’s own marketing page.
A Systemic Problem
The rise of such predatory actors suggests that the ransomware economy has become a self-sustaining ecosystem of exploitation. It is no longer just about the hackers; it is about a secondary layer of "professional" criminals who act as parasites on the victimized organizations.
As the legal proceedings against Zohar Pinhasi move forward, the cybersecurity industry is forced to confront a difficult reality: the existence of "remediation" firms that are, in effect, extensions of the ransomware threat actors themselves. For the victims, the ordeal of a ransomware attack is no longer just about the loss of data or the cost of the ransom—it is about navigating a market where the lines between helper and predator have been intentionally blurred.
For the Justice Department, this prosecution is part of a larger, ongoing effort to clean up the incident response industry. By holding figures like Pinhasi accountable, the government aims to send a clear message: those who choose to monetize the suffering of others by operating in the shadows will eventually be brought into the light of the courtroom. As the trial looms, the tech community will be watching closely, hoping this case serves as a definitive turning point in the professionalization—and purification—of cybersecurity response services.

 Nana Muazin
 Ali Ikhwan

 Dwi Wanna

 Muslim

 Nana Wu


 Rifan Muazin
 Asro
