
 Dwi Wanna
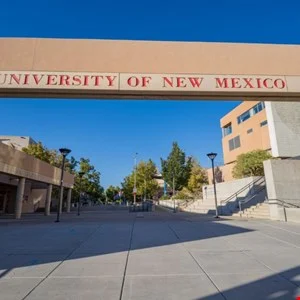
The University of New Mexico Health Sciences Center (UNM HSC)—a cornerstone of healthcare delivery and medical research in the American Southwest—recently faced a debilitating cyber-incident that paralyzed its clinical operations, forced the diversion of emergency services, and compromised a vast repository of sensitive data. The event serves as a stark reminder of the escalating vulnerability of academic medical centers (AMCs) to organized cyber-criminal syndicates.
As the institution grapples with the aftermath of the intrusion, the healthcare community is left to reckon with the reality that, for modern hospitals, cybersecurity is no longer an IT concern—it is a matter of patient safety and public health.
The Anatomy of the Crisis: Main Facts
The breach was first identified on the afternoon of Monday, October 26. The impact was immediate and severe. Recognizing that their clinical systems—including electronic health records (EHRs) and scheduling software—had been compromised, UNM HSC leadership took the drastic step of halting all non-emergency operations.
The incident necessitated the cancellation of all scheduled surgeries and outpatient appointments for the remainder of the day. Perhaps most concerningly, the hospital was forced to divert ambulances, pushing the burden of emergency care onto surrounding healthcare providers and straining regional infrastructure.
While the facility began a phased restoration of its systems by the following day, the operational impact extended well beyond the hospital wards. The breach triggered a campus-wide lockdown of IT services, forcing the closure of the School of Medicine, the College of Pharmacy, the College of Nursing, and the College of Population Health. Thousands of students were sent home, and both in-person and remote classes were suspended as the institution’s incident response team worked to isolate the threat.
Chronology of the Incident
The following timeline details the rapid escalation and subsequent mitigation efforts taken by the university:
- Monday, October 26, 2:30 PM MDT: UNM HSC publicly discloses a major cybersecurity incident. Immediate instructions are issued for patients to avoid facilities and for emergency cases to be redirected via 911.
- Monday, October 26, Afternoon/Evening: Administrative and educational operations are suspended. Non-essential employees are instructed to stay home, and all Health Sciences classes are canceled.
- Monday, October 26, 10:27 PM MDT: UNM HSC issues a secondary update confirming that hospitals have reopened and that clinical services will resume on a phased basis starting Tuesday, October 27.
- Tuesday, October 27: Clinical operations begin a return to normalcy. However, the educational arm of the Health Sciences Center remains closed, with all classes (remote and in-person) suspended for the day to allow for continued network remediation.
- Ongoing Post-Incident: The university transitions into a long-term recovery phase, involving forensic investigation, data impact assessments, and the notification of affected parties.
The Adversary: Who is "BYOD"?
While initial reports were sparse regarding the perpetrators, the emerging ransomware group known as "BYOD" (Bring Your Own Device) has claimed responsibility. Intelligence gathered by the cybersecurity firm VenariX confirms that the group listed the University of New Mexico on its dark web data leak site.
BYOD’s claims are chilling in their scope. The group alleges that it successfully compromised 36,000 machines within the university’s network. They claim to have exfiltrated a massive trove of sensitive information, including:
- Personally Identifiable Information (PII) of students and staff.
- University research data.
- Internal institutional records and sensitive correspondence.
In a bold message posted to their leak site, the group declared, "This is your entire network and infrastructure compromised, the entire university COMPLETELY." If these claims are verified, the incident represents a catastrophic failure of the university’s perimeter security and internal segmentation.
Supporting Data: The Scale of the Impact
To understand the magnitude of this disruption, one must consider the sheer volume of activity occurring at UNM HSC on any given day. The facility serves as the state’s primary teaching hospital and a major provider of tertiary care.
- Patient Volume: UNM HSC processes over one million patient visits annually, consisting of roughly 900,000 outpatient appointments and 100,000 emergency room encounters. The diversion of ambulances and the cancellation of surgeries meant that hundreds, if not thousands, of patients were denied timely care during the outage.
- Student Population: As of 2025, the Health Sciences Center served approximately 2,670 students. The cancellation of classes, while necessary for network isolation, represents a significant disruption to medical and nursing education.
- Network Footprint: The attackers’ claim of 36,000 compromised machines highlights the expansive, often porous nature of university networks. AMCs are particularly vulnerable because they must support a diverse ecosystem of high-speed research equipment, administrative workstations, student devices, and medical IoT devices, all while maintaining the stringent privacy requirements of HIPAA.
Official Responses and Remediation
The university’s response was characterized by a rapid shift from operational maintenance to emergency containment. In their public disclosures, UNM HSC emphasized that the safety of patients and the integrity of their data remained the highest priority.
"At 2:30 PM, UNM Health began resuming operations and bringing systems back online in phases, as it was safe to do so," the university stated in its follow-up announcement. "We will work with patients to reschedule missed appointments and procedures."
The decision to keep the educational campuses closed even after clinical services resumed underscores the complexity of the remediation. In a modern network, "cleaning" a system is not as simple as a reboot; it requires extensive forensic scrubbing to ensure that persistence mechanisms—often left by ransomware actors to regain access later—are fully eradicated.
Implications: The Growing Threat to Academic Medicine
The incident at UNM HSC is not an isolated event; it is a symptom of a broader, systemic threat facing the global healthcare sector.
The Convergence of Research and Care
Academic medical centers are uniquely attractive targets. They house intellectual property (research data) that is valuable to state-sponsored actors and cybercriminals alike, while simultaneously maintaining the clinical systems that are critical to life-saving operations. Attackers know that if they disable the hospital, they create immense pressure for the victim to pay a ransom to restore operations immediately.
The Financial and Reputational Burden
Beyond the immediate costs of remediation—which often involve hiring third-party incident response firms, performing forensic audits, and implementing new security controls—the long-term impact on patient trust is difficult to quantify. When sensitive medical and student data is exfiltrated, the institution faces potential legal liability, regulatory fines (such as those under HIPAA), and a permanent stain on its reputation.
The "BYOD" Paradigm Shift
The group’s name, "BYOD," ironically points to one of the biggest challenges in university security: the "Bring Your Own Device" phenomenon. In an academic environment, students and staff frequently connect personal devices to the institutional network. If these devices are not strictly managed through Zero Trust architectures, they become "patient zero" for ransomware infections, allowing attackers to pivot laterally into the highly secured environments where patient data resides.
Conclusion: Lessons for the Future
The UNM HSC cyberattack serves as a sobering case study. The fact that an entire university system could be brought to its knees suggests that the traditional approach to perimeter defense is no longer sufficient.
As we look toward the future of healthcare cybersecurity, three priorities emerge:
- Network Segmentation: Critical clinical systems must be air-gapped or strictly segmented from general university networks to ensure that a student’s compromised laptop cannot lead to a hospital-wide outage.
- Incident Response Preparedness: The swiftness with which UNM HSC shifted to manual/phased operations suggests that their emergency response planning was effective, but the duration of the outage highlights the need for more resilient, offline-capable clinical documentation systems.
- Investment in Human Factors: With phishing and credential harvesting remaining the most common entry points for groups like BYOD, consistent training for staff and students is the first line of defense.
The incident at the University of New Mexico is a call to action. While clinical services have resumed, the forensic analysis and the recovery of compromised data will continue for months. For the rest of the academic and medical community, the message is clear: the threat is evolving, and only those who treat cybersecurity as a core component of their clinical mission will be able to withstand the next wave of digital aggression.

 Suro Senen
 Lina Hope
 Nana Muazin
 Pevita Pearce
 Nila Kartika Wati
 Azzam Bilal Chamdy
